

Ferret
Ferret
Get Started with Apps!
Get Started with Apps!
App Version:
2026.11.4
(Changelog)
Keywords: inventory, home, warranty, insurance, barcode, labels
Train: Community
Home Page: https://github.com/ferret-project/ferret
Keywords: inventory, home, warranty, insurance, barcode, labels
Train: Community
Home Page: https://github.com/ferret-project/ferret
Ferret Details
Added: 2026-11-06
Last Updated: 2026-11-06
Added: 2026-11-06
Last Updated: 2026-11-06
Self-hosted home inventory for the whole family. Add things by photo, barcode or a walk through a room, find them by what they are, print QR labels, and keep warranties, manuals, maintenance and an insurance report. REST API and MCP server; optional AI on your own models.
Run as Context- Container [ferret] can run as any non-root user and group.
Group: 568 / Host group is [apps]
User: 568 / Host user is [apps]
Screenshots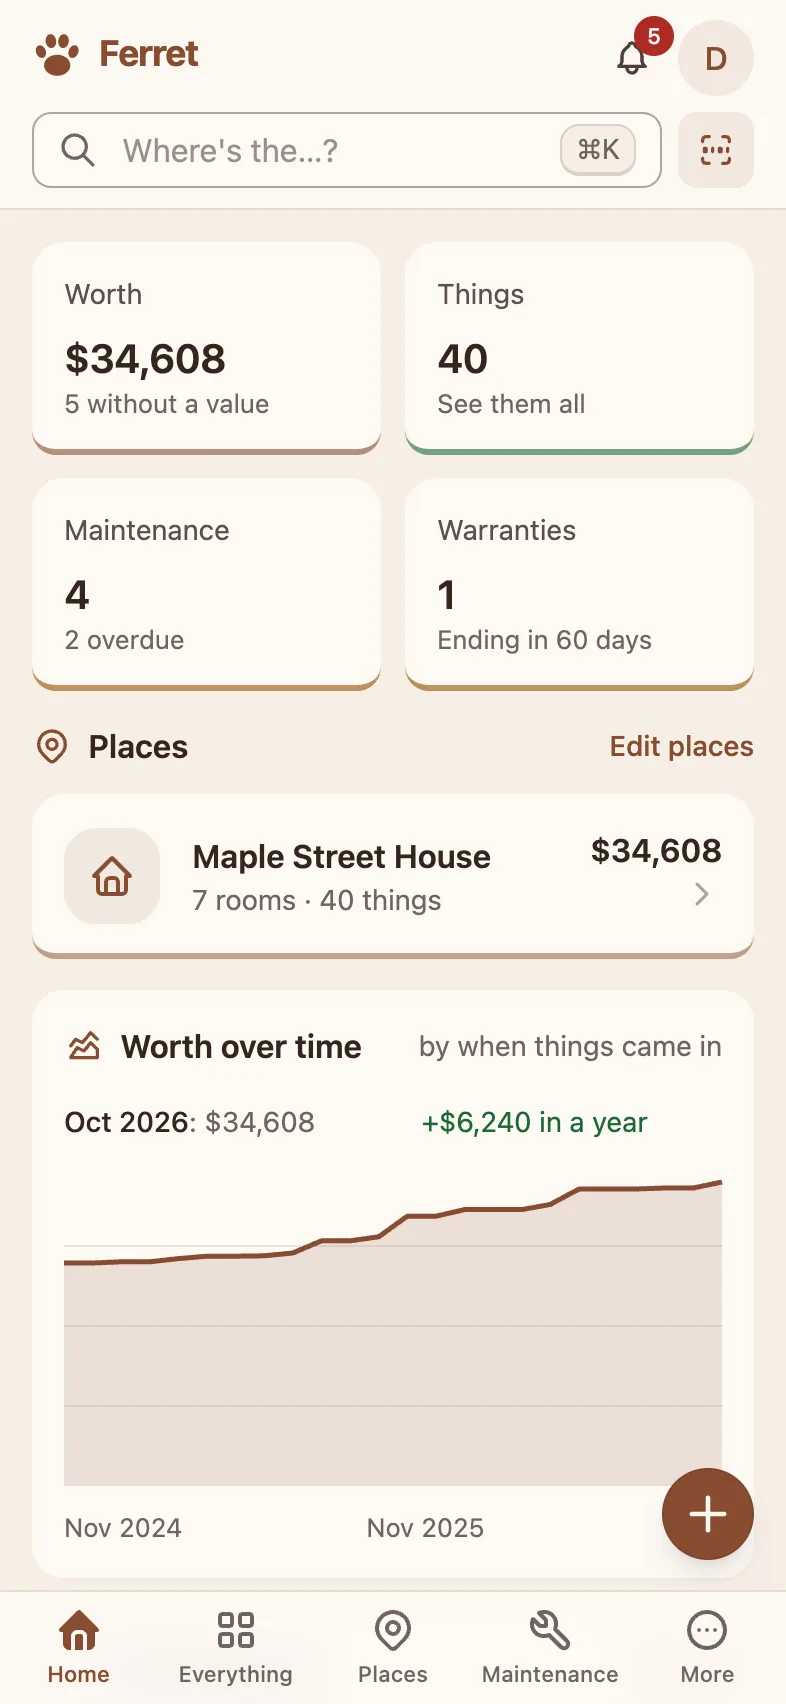
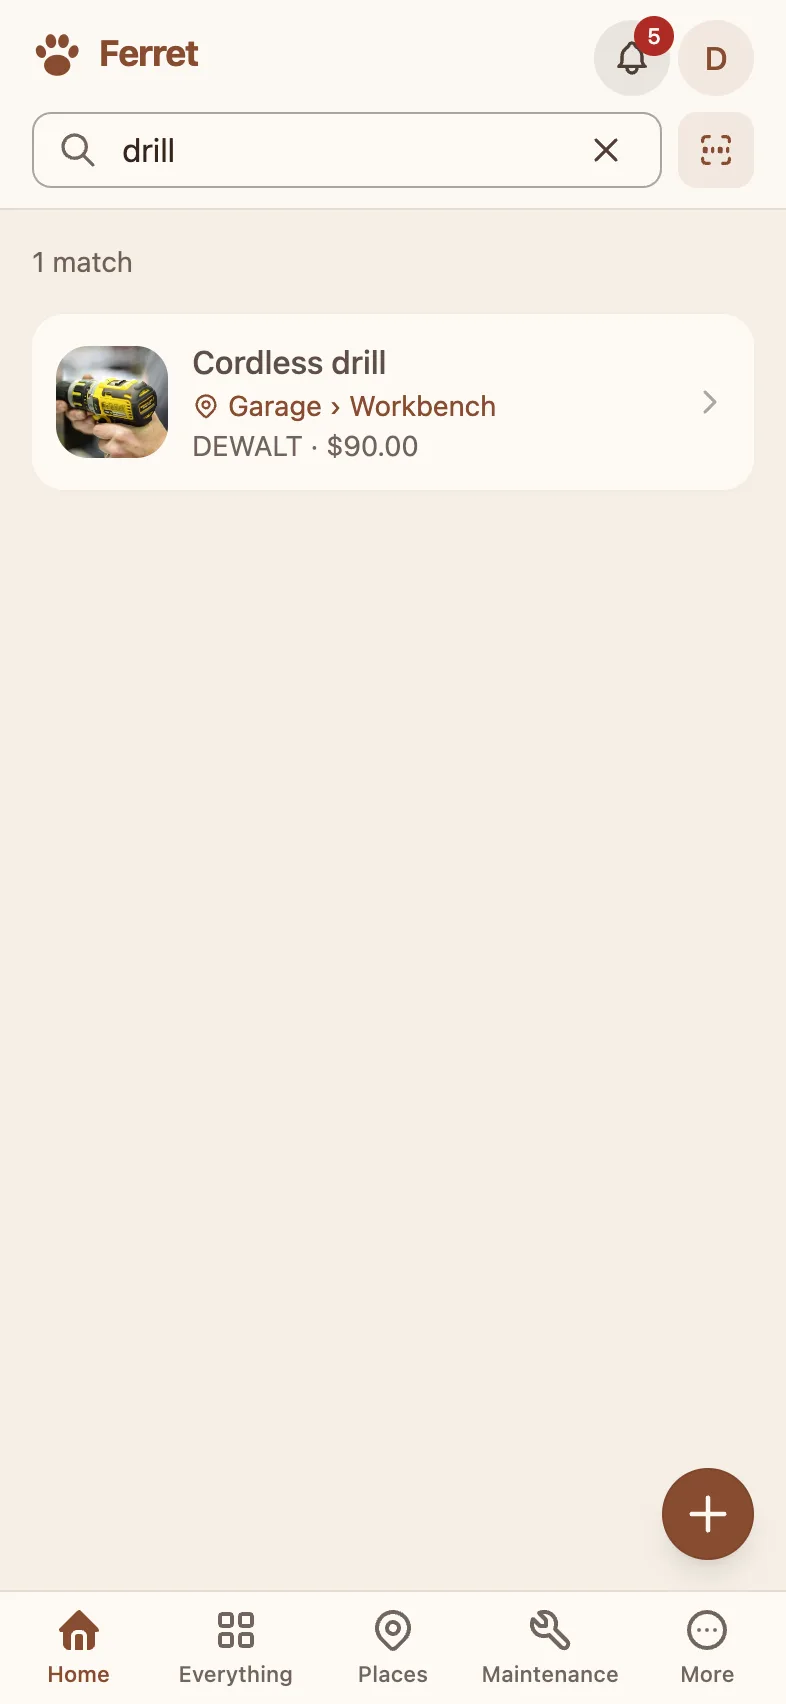
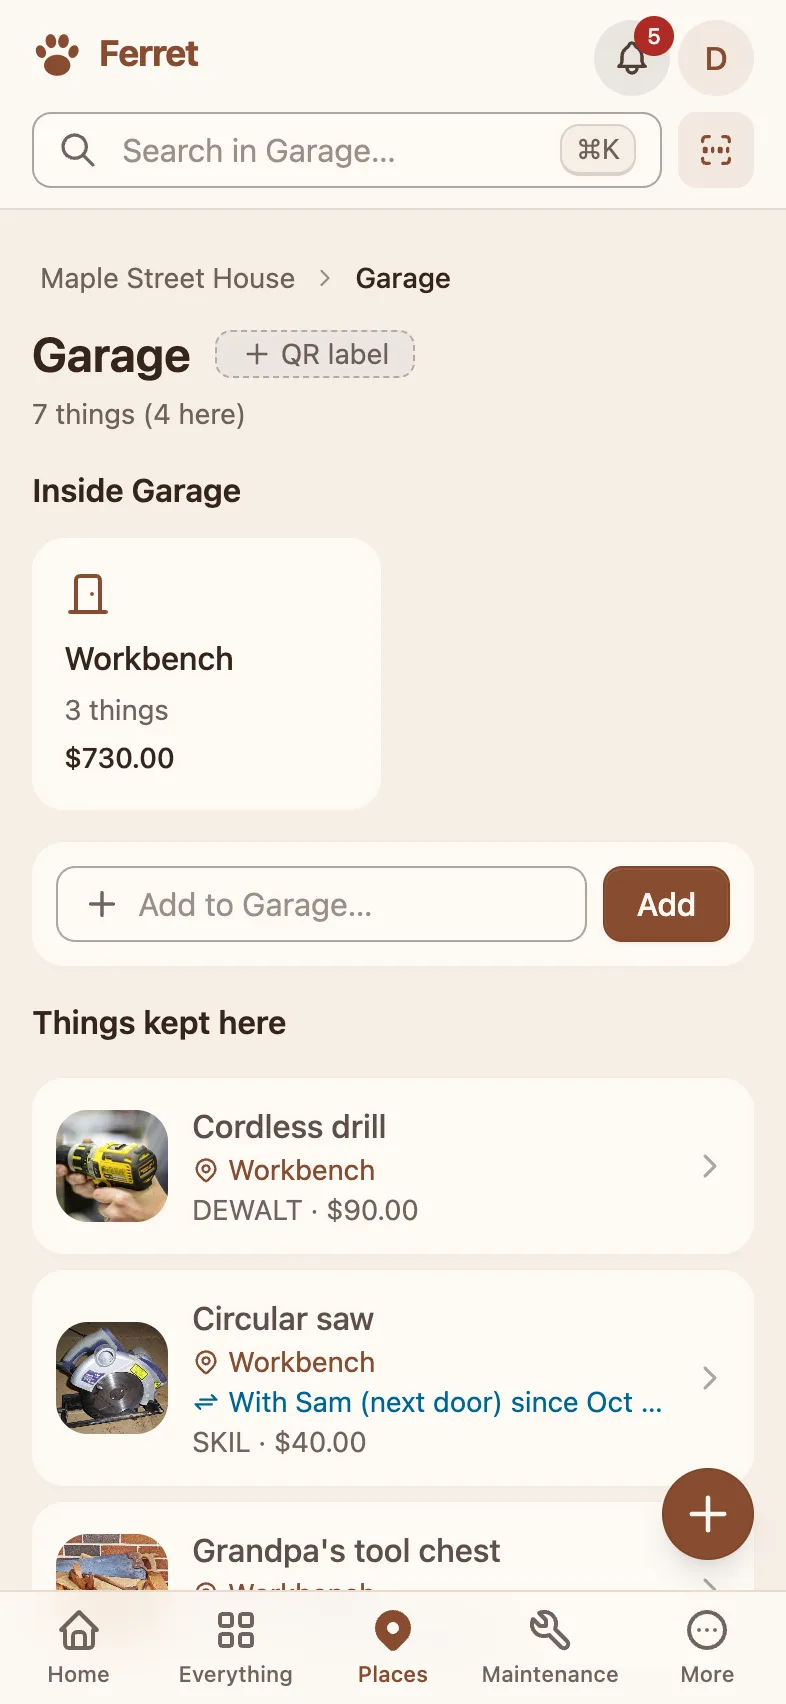
×
![Full Screenshot]()
App Metadata (Raw File)
{
"1.0.1": {
"healthy": true,
"supported": true,
"healthy_error": null,
"location": "/__w/apps/apps/trains/community/ferret/1.0.1",
"last_update": "2026-11-06 16:12:24",
"required_features": [],
"human_version": "2026.11.4_1.0.1",
"version": "1.0.1",
"app_metadata": {
"app_version": "2026.11.4",
"capabilities": [],
"categories": [
"productivity"
],
"changelog_url": "https://github.com/ferret-project/ferret/releases",
"date_added": "2026-11-06",
"description": "Self-hosted home inventory for the whole family. Add things by photo, barcode or a walk through a room, find them by what they are, print QR labels, and keep warranties, manuals, maintenance and an insurance report. REST API and MCP server; optional AI on your own models.",
"home": "https://github.com/ferret-project/ferret",
"host_mounts": [],
"icon": "https://media.sys.truenas.net/apps/ferret/icons/icon.png",
"keywords": [
"inventory",
"home",
"warranty",
"insurance",
"barcode",
"labels"
],
"lib_version": "2.3.18",
"lib_version_hash": "ed9839f681342ae8ca5f8c4c860ae22d0845a0919f472ba780d6edbc838f2633",
"maintainers": [
{
"email": "dev@truenas.com",
"name": "truenas",
"url": "https://www.truenas.com/"
}
],
"name": "ferret",
"run_as_context": [
{
"description": "Container [ferret] can run as any non-root user and group.",
"gid": 568,
"group_name": "Host group is [apps]",
"uid": 568,
"user_name": "Host user is [apps]"
}
],
"screenshots": [
"https://media.sys.truenas.net/apps/ferret/screenshots/screenshot1.webp",
"https://media.sys.truenas.net/apps/ferret/screenshots/screenshot2.webp",
"https://media.sys.truenas.net/apps/ferret/screenshots/screenshot3.webp"
],
"sources": [
"https://apps.truenas.com/catalog/ferret_community/",
"https://github.com/ferret-project/ferret"
],
"title": "Ferret",
"train": "community",
"version": "1.0.1"
},
"schema": {
"groups": [
{
"name": "Ferret Configuration",
"description": "Configure Ferret"
},
{
"name": "User and Group Configuration",
"description": "Configure User and Group for Ferret"
},
{
"name": "Network Configuration",
"description": "Configure Network for Ferret"
},
{
"name": "Storage Configuration",
"description": "Configure Storage for Ferret"
},
{
"name": "Labels Configuration",
"description": "Configure Labels for Ferret"
},
{
"name": "Resources Configuration",
"description": "Configure Resources for Ferret"
}
],
"questions": [
{
"variable": "ferret",
"label": "",
"group": "Ferret Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "public_url",
"label": "Public URL",
"description": "The address people (and AI assistants, over MCP) use to reach Ferret.</br>\nBehind a reverse proxy, its HTTPS address (for example https://ferret.example.com);</br>\notherwise the NAS address and port (for example http://192.168.1.10:30558).</br>\nInstalling on a phone, the camera and push notifications need HTTPS.\n",
"schema": {
"type": "uri",
"default": "",
"required": true
}
},
{
"variable": "auth_secret",
"label": "Auth Secret",
"description": "Signs sign-ins and seals two-step sign-in. 32 or more random characters (openssl rand -base64 32).\n",
"schema": {
"type": "string",
"default": "",
"required": true,
"private": true,
"valid_chars": "^.{32,}$",
"valid_chars_error": "Use 32 characters or more (openssl rand -base64 32)."
}
},
{
"variable": "files_key",
"label": "Files Key",
"description": "The key every photo, document and backup is sealed with: 32 random bytes in base64 (openssl rand -base64 32).</br>\nKeep a copy off the server: without it, uploaded files and backups can't be read, and it can't be changed\nonce files are sealed.\n",
"schema": {
"type": "string",
"default": "",
"required": true,
"private": true,
"valid_chars": "^[A-Za-z0-9+/]{43}=$",
"valid_chars_error": "Use 32 random bytes in base64 (openssl rand -base64 32)."
}
},
{
"variable": "allow_signup",
"label": "Allow Sign-up",
"description": "Anyone who can reach Ferret may make an account (everyone after the first confirms their email, which needs</br>\nMAIL_URL and APPRISE_URL). Turn it off once your household is in: invited people can still join from their link.\n",
"schema": {
"type": "boolean",
"default": true
}
},
{
"variable": "vapid_subject",
"label": "Push Contact (optional)",
"description": "Push notifications work without setup. Apple's push service (iPhones, iPads, Safari) needs a contact on a</br>\npublic domain, e.g. mailto:you@example.com \u2014 without one, push reaches only other browsers when Ferret is</br>\nreached by a local name or address. Leave empty to use admin@ the Public URL's host.\n",
"schema": {
"type": "string",
"default": "",
"valid_chars": "^(mailto:[^@\\s]+@[^@\\s]+|https://\\S+)$",
"valid_chars_error": "Use mailto:you@example.com or an https:// address."
}
},
{
"variable": "trusted_proxies",
"label": "Trusted Proxies",
"description": "Behind a reverse proxy: its IP addresses or CIDR ranges, so visitors' own addresses are believed from it</br>\nand nobody else. Leave empty without one.\n",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "proxy",
"label": "Proxy",
"schema": {
"type": "string",
"default": "",
"required": true
}
}
]
}
},
{
"variable": "additional_envs",
"label": "Additional Environment Variables",
"description": "Optional features switch on when their settings are present (Ferret's help at /docs/hosting/configuration):</br>\nemail (APPRISE_URL, MAIL_URL), backup schedule (BACKUP_HOUR, BACKUP_KEEP),</br>\nAI on your own models (OLLAMA_URL, CHAT_URL, QDRANT_URL, DOCLING_URL), barcode lookups</br>\n(BARCODE_LOOKUP=upcitemdb), push (VAPID_PUBLIC_KEY, VAPID_PRIVATE_KEY), single sign-on (OIDC_ISSUER, ...).\n",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "env",
"label": "Environment Variable",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Name",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "value",
"label": "Value",
"schema": {
"type": "string"
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "run_as",
"label": "",
"group": "User and Group Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "user",
"label": "User ID",
"description": "The user id that Ferret files will be owned by.",
"schema": {
"type": "int",
"min": 568,
"default": 568,
"required": true
}
},
{
"variable": "group",
"label": "Group ID",
"description": "The group id that Ferret files will be owned by.",
"schema": {
"type": "int",
"min": 568,
"default": 568,
"required": true
}
}
]
}
},
{
"variable": "network",
"label": "",
"group": "Network Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "web_port",
"label": "WebUI Port",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "bind_mode",
"label": "Port Bind Mode",
"description": "The port bind mode.</br>\n- Publish: The port will be published on the host for external access.</br>\n- Expose: The port will be exposed for inter-container communication.</br>\n- None: The port will not be exposed or published.</br>\nNote: If the Dockerfile defines an EXPOSE directive,\nthe port will still be exposed for inter-container communication regardless of this setting.\n",
"schema": {
"type": "string",
"default": "published",
"enum": [
{
"value": "published",
"description": "Publish port on the host for external access"
},
{
"value": "exposed",
"description": "Expose port for inter-container communication"
},
{
"value": "",
"description": "None"
}
]
}
},
{
"variable": "port_number",
"label": "Port Number",
"schema": {
"type": "int",
"default": 30558,
"min": 1,
"max": 65535,
"required": true
}
},
{
"variable": "host_ips",
"label": "Host IPs",
"description": "IPs on the host to bind this port",
"schema": {
"type": "list",
"show_if": [
[
"bind_mode",
"=",
"published"
]
],
"default": [],
"items": [
{
"variable": "host_ip",
"label": "Host IP",
"schema": {
"type": "string",
"required": true,
"$ref": [
"definitions/node_bind_ip"
]
}
}
]
}
}
]
}
},
{
"variable": "networks",
"label": "Networks",
"description": "The docker networks to join",
"schema": {
"type": "list",
"show_if": [
[
"host_network",
"=",
false
]
],
"default": [],
"items": [
{
"variable": "network",
"label": "Network",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Name",
"description": "The name of the network to join.</br>\nThe network must already exist.\n",
"schema": {
"type": "string",
"default": "",
"required": true
}
},
{
"variable": "containers",
"label": "Containers",
"description": "The containers to add to this network.",
"schema": {
"type": "list",
"items": [
{
"variable": "container",
"label": "Container",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Container Name",
"schema": {
"type": "string",
"required": true,
"enum": [
{
"value": "ferret",
"description": "ferret"
}
]
}
},
{
"variable": "config",
"label": "Container Network Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "aliases",
"label": "Aliases (Optional)",
"description": "The network aliases to use for this container on this network.",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "alias",
"label": "Alias",
"schema": {
"type": "string"
}
}
]
}
},
{
"variable": "interface_name",
"label": "Interface Name (Optional)",
"description": "The network interface name to use for this network",
"schema": {
"type": "string"
}
},
{
"variable": "mac_address",
"label": "MAC Address (Optional)",
"description": "The MAC address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "ipv4_address",
"label": "IPv4 Address (Optional)",
"description": "The IPv4 address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "ipv6_address",
"label": "IPv6 Address (Optional)",
"description": "The IPv6 address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "gw_priority",
"label": "Gateway Priority (Optional)",
"description": "Indicates the priority of the gateway for this network interface.",
"schema": {
"type": "int",
"null": true
}
},
{
"variable": "priority",
"label": "Priority (Optional)",
"description": "Indicates in which order Compose connects the service\u2019s containers to its networks.",
"schema": {
"type": "int",
"null": true
}
}
]
}
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "host_network",
"label": "Host Network",
"description": "Bind to the host network. It's recommended to keep this disabled.\n",
"schema": {
"type": "boolean",
"default": false
}
}
]
}
},
{
"variable": "storage",
"label": "",
"group": "Storage Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "data",
"label": "Data Storage",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "type",
"label": "Type",
"description": "ixVolume: Is dataset created automatically by the system.</br>\nHost Path: Is a path that already exists on the system.\n",
"schema": {
"type": "string",
"required": true,
"default": "ix_volume",
"enum": [
{
"value": "host_path",
"description": "Host Path (Path that already exists on the system)"
},
{
"value": "ix_volume",
"description": "ixVolume (Dataset created automatically by the system)"
}
]
}
},
{
"variable": "ix_volume_config",
"label": "ixVolume Configuration",
"description": "The configuration for the ixVolume dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"ix_volume"
]
],
"$ref": [
"normalize/ix_volume"
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "dataset_name",
"label": "Dataset Name",
"description": "The name of the dataset to use for storage.",
"schema": {
"type": "string",
"required": true,
"hidden": true,
"default": "data"
}
},
{
"variable": "acl_entries",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": []
}
}
]
}
},
{
"variable": "host_path_config",
"label": "Host Path Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"host_path"
]
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "acl",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
},
{
"variable": "path",
"label": "Host Path",
"description": "The host path to use for storage.",
"schema": {
"type": "hostpath",
"show_if": [
[
"acl_enable",
"=",
false
]
],
"required": true
}
}
]
}
}
]
}
},
{
"variable": "backups",
"label": "Backups Storage",
"description": "Ferret's nightly backups (encrypted with the Files Key, checked after each run) go here.</br>\nPrefer a path on another pool or machine than the data storage.</br>\nBACKUP_HOUR (default 3) and BACKUP_KEEP (default 14) can be set in Additional Environment Variables.\n",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "type",
"label": "Type",
"description": "ixVolume: Is dataset created automatically by the system.</br>\nHost Path: Is a path that already exists on the system.\n",
"schema": {
"type": "string",
"required": true,
"default": "ix_volume",
"enum": [
{
"value": "host_path",
"description": "Host Path (Path that already exists on the system)"
},
{
"value": "ix_volume",
"description": "ixVolume (Dataset created automatically by the system)"
}
]
}
},
{
"variable": "ix_volume_config",
"label": "ixVolume Configuration",
"description": "The configuration for the ixVolume dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"ix_volume"
]
],
"$ref": [
"normalize/ix_volume"
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "dataset_name",
"label": "Dataset Name",
"description": "The name of the dataset to use for storage.",
"schema": {
"type": "string",
"required": true,
"hidden": true,
"default": "backups"
}
},
{
"variable": "acl_entries",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": []
}
}
]
}
},
{
"variable": "host_path_config",
"label": "Host Path Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"host_path"
]
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "acl",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
},
{
"variable": "path",
"label": "Host Path",
"description": "The host path to use for storage.",
"schema": {
"type": "hostpath",
"show_if": [
[
"acl_enable",
"=",
false
]
],
"required": true
}
}
]
}
}
]
}
},
{
"variable": "additional_storage",
"label": "Additional Storage",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "storage_entry",
"label": "Storage Entry",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "type",
"label": "Type",
"description": "ixVolume: Is dataset created automatically by the system.</br>\nHost Path: Is a path that already exists on the system.</br>\nSMB Share: Is a SMB share that is mounted to as a volume.</br>\nNFS Share: Is a NFS share that is mounted to as a volume.\n",
"schema": {
"type": "string",
"required": true,
"default": "ix_volume",
"enum": [
{
"value": "host_path",
"description": "Host Path (Path that already exists on the system)"
},
{
"value": "ix_volume",
"description": "ixVolume (Dataset created automatically by the system)"
},
{
"value": "cifs",
"description": "SMB/CIFS Share (Mounts a volume to a SMB share)"
},
{
"value": "nfs",
"description": "NFS Share (Mounts a volume to a NFS share)"
}
]
}
},
{
"variable": "read_only",
"label": "Read Only",
"description": "Mount the volume as read only.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "mount_path",
"label": "Mount Path",
"description": "The path inside the container to mount the storage.",
"schema": {
"type": "path",
"required": true
}
},
{
"variable": "host_path_config",
"label": "Host Path Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"host_path"
]
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "acl",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
},
{
"variable": "path",
"label": "Host Path",
"description": "The host path to use for storage.",
"schema": {
"type": "hostpath",
"show_if": [
[
"acl_enable",
"=",
false
]
],
"required": true
}
}
]
}
},
{
"variable": "ix_volume_config",
"label": "ixVolume Configuration",
"description": "The configuration for the ixVolume dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"ix_volume"
]
],
"$ref": [
"normalize/ix_volume"
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "dataset_name",
"label": "Dataset Name",
"description": "The name of the dataset to use for storage.",
"schema": {
"type": "string",
"required": true,
"default": "storage_entry"
}
},
{
"variable": "acl_entries",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
}
]
}
},
{
"variable": "cifs_config",
"label": "SMB Configuration",
"description": "The configuration for the SMB dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"cifs"
]
],
"attrs": [
{
"variable": "server",
"label": "Server",
"description": "The server to mount the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "path",
"label": "Path",
"description": "The path to mount the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "username",
"label": "Username",
"description": "The username to use for the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "password",
"label": "Password",
"description": "The password to use for the SMB share.",
"schema": {
"type": "string",
"required": true,
"private": true
}
},
{
"variable": "domain",
"label": "Domain",
"description": "The domain to use for the SMB share.",
"schema": {
"type": "string"
}
}
]
}
},
{
"variable": "nfs_config",
"label": "NFS Configuration",
"description": "The configuration for the NFS dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"nfs"
]
],
"attrs": [
{
"variable": "server",
"label": "Server",
"description": "The server to mount the NFS share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "path",
"label": "Path",
"description": "The path to mount the NFS share.",
"schema": {
"type": "string",
"required": true
}
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "labels",
"label": "",
"group": "Labels Configuration",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "label",
"label": "Label",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "key",
"label": "Key",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "value",
"label": "Value",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "containers",
"label": "Containers",
"description": "Containers where the label should be applied",
"schema": {
"type": "list",
"items": [
{
"variable": "container",
"label": "Container",
"schema": {
"type": "string",
"required": true,
"enum": [
{
"value": "ferret",
"description": "ferret"
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "resources",
"label": "",
"group": "Resources Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "limits",
"label": "Limits",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "cpus",
"label": "CPUs",
"description": "CPUs limit for Ferret.",
"schema": {
"type": "int",
"default": 2,
"required": true
}
},
{
"variable": "memory",
"label": "Memory (in MB)",
"description": "Memory limit for Ferret.",
"schema": {
"type": "int",
"default": 4096,
"required": true
}
}
]
}
}
]
}
}
]
},
"readme": "<h1>Ferret</h1> <p><a href=\"https://github.com/ferret-project/ferret\">Ferret</a> is a self-hosted home inventory: find anything you own.</p>",
"changelog": null,
"chart_metadata": {
"app_version": "2026.11.4",
"capabilities": [],
"categories": [
"productivity"
],
"changelog_url": "https://github.com/ferret-project/ferret/releases",
"date_added": "2026-11-06",
"description": "Self-hosted home inventory for the whole family. Add things by photo, barcode or a walk through a room, find them by what they are, print QR labels, and keep warranties, manuals, maintenance and an insurance report. REST API and MCP server; optional AI on your own models.",
"home": "https://github.com/ferret-project/ferret",
"host_mounts": [],
"icon": "https://media.sys.truenas.net/apps/ferret/icons/icon.png",
"keywords": [
"inventory",
"home",
"warranty",
"insurance",
"barcode",
"labels"
],
"lib_version": "2.3.18",
"lib_version_hash": "ed9839f681342ae8ca5f8c4c860ae22d0845a0919f472ba780d6edbc838f2633",
"maintainers": [
{
"email": "dev@truenas.com",
"name": "truenas",
"url": "https://www.truenas.com/"
}
],
"name": "ferret",
"run_as_context": [
{
"description": "Container [ferret] can run as any non-root user and group.",
"gid": 568,
"group_name": "Host group is [apps]",
"uid": 568,
"user_name": "Host user is [apps]"
}
],
"screenshots": [
"https://media.sys.truenas.net/apps/ferret/screenshots/screenshot1.webp",
"https://media.sys.truenas.net/apps/ferret/screenshots/screenshot2.webp",
"https://media.sys.truenas.net/apps/ferret/screenshots/screenshot3.webp"
],
"sources": [
"https://apps.truenas.com/catalog/ferret_community/",
"https://github.com/ferret-project/ferret"
],
"title": "Ferret",
"train": "community",
"version": "1.0.1"
}
}
}Support, maintenance, and documentation for applications within the Community catalog is handled by the TrueNAS community. The TrueNAS Applications Market hosts but does not validate or maintain any linked resources associated with this app.
There currently aren’t any resources available for this application!
Please help the TrueNAS community add resources here or discuss this application in the TrueNAS Community forum.