

KTN Enclosure Manager
KTN Enclosure Manager
Get Started with Apps!
Get Started with Apps!
App Version:
1.6.3
(Changelog)
Keywords: enclosure, ses, sas, jbod, disk-shelf, identify
Train: Community
Home Page: https://github.com/MechanicalCoderX/ktn-enclosure-manager
Keywords: enclosure, ses, sas, jbod, disk-shelf, identify
Train: Community
Home Page: https://github.com/MechanicalCoderX/ktn-enclosure-manager
KTN Enclosure Manager Details
Added: 2026-11-17
Last Updated: 2026-11-18
Added: 2026-11-17
Last Updated: 2026-11-18
Physical drive-bay map, chassis telemetry and IDENT LED control for SES disk shelves attached to TrueNAS SCALE.
Run as Context- Container [ktn-enclosure-manager] runs as root user and group.
Group: 0 / Host group is [root]
User: 0 / Host user is [root]
Screenshots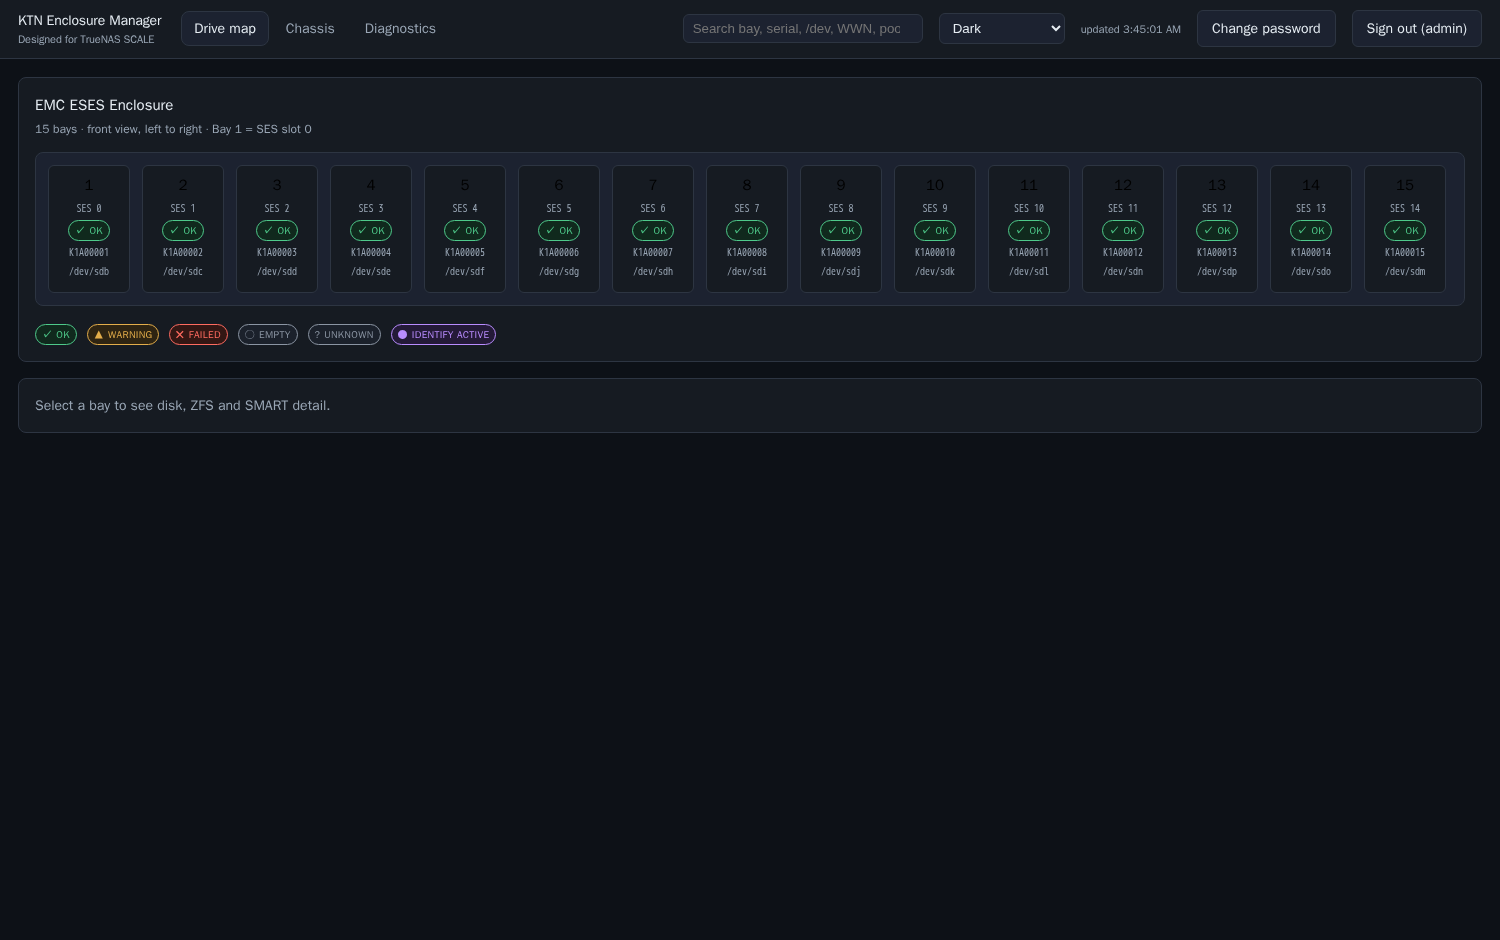
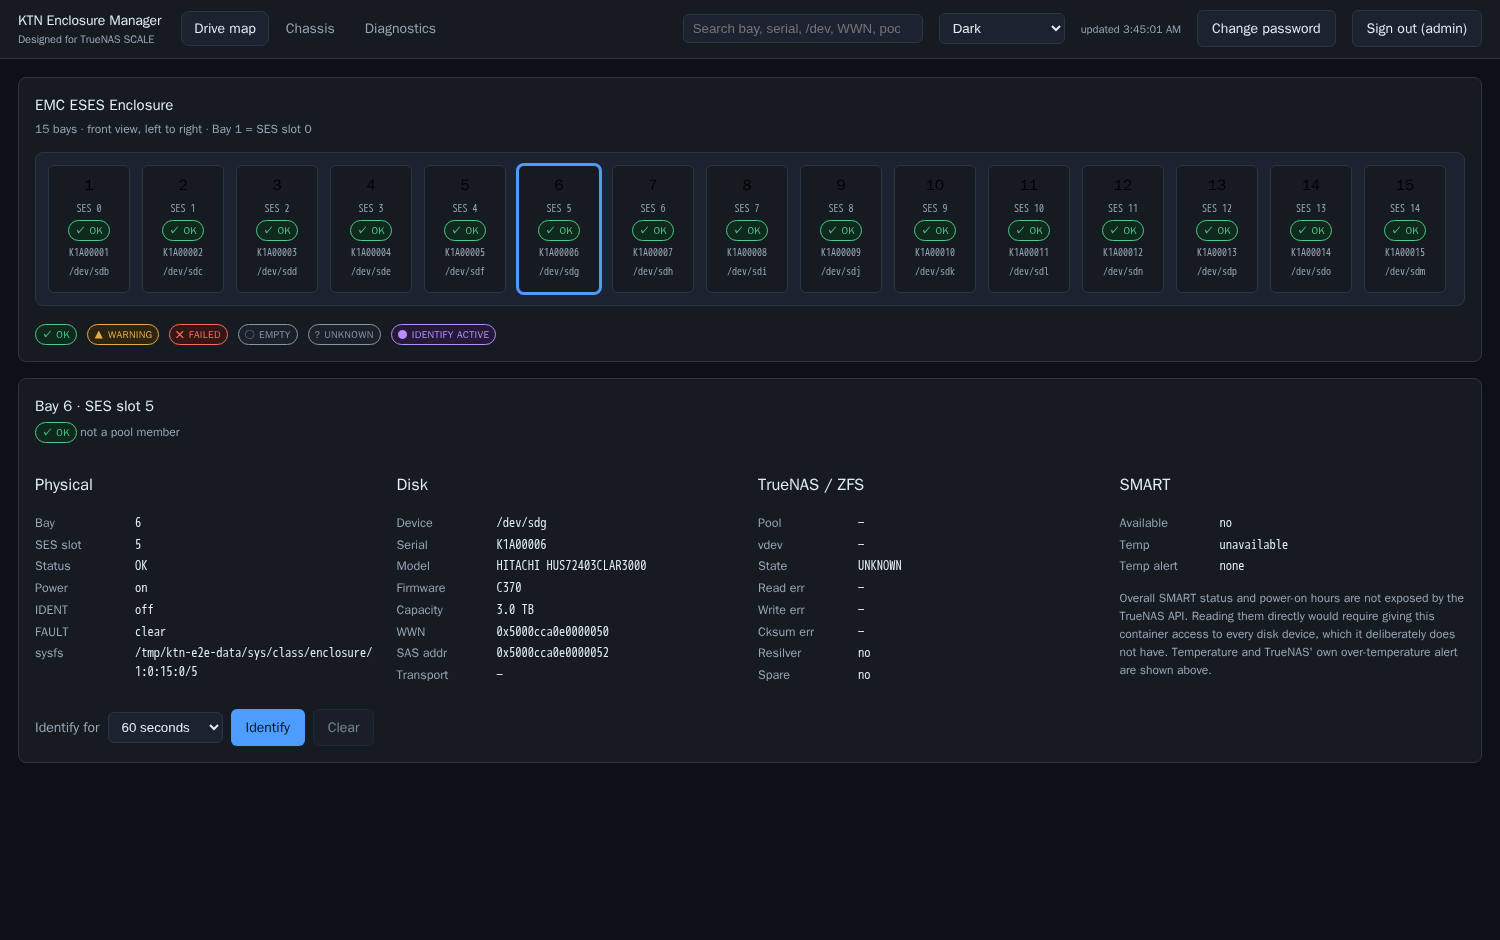
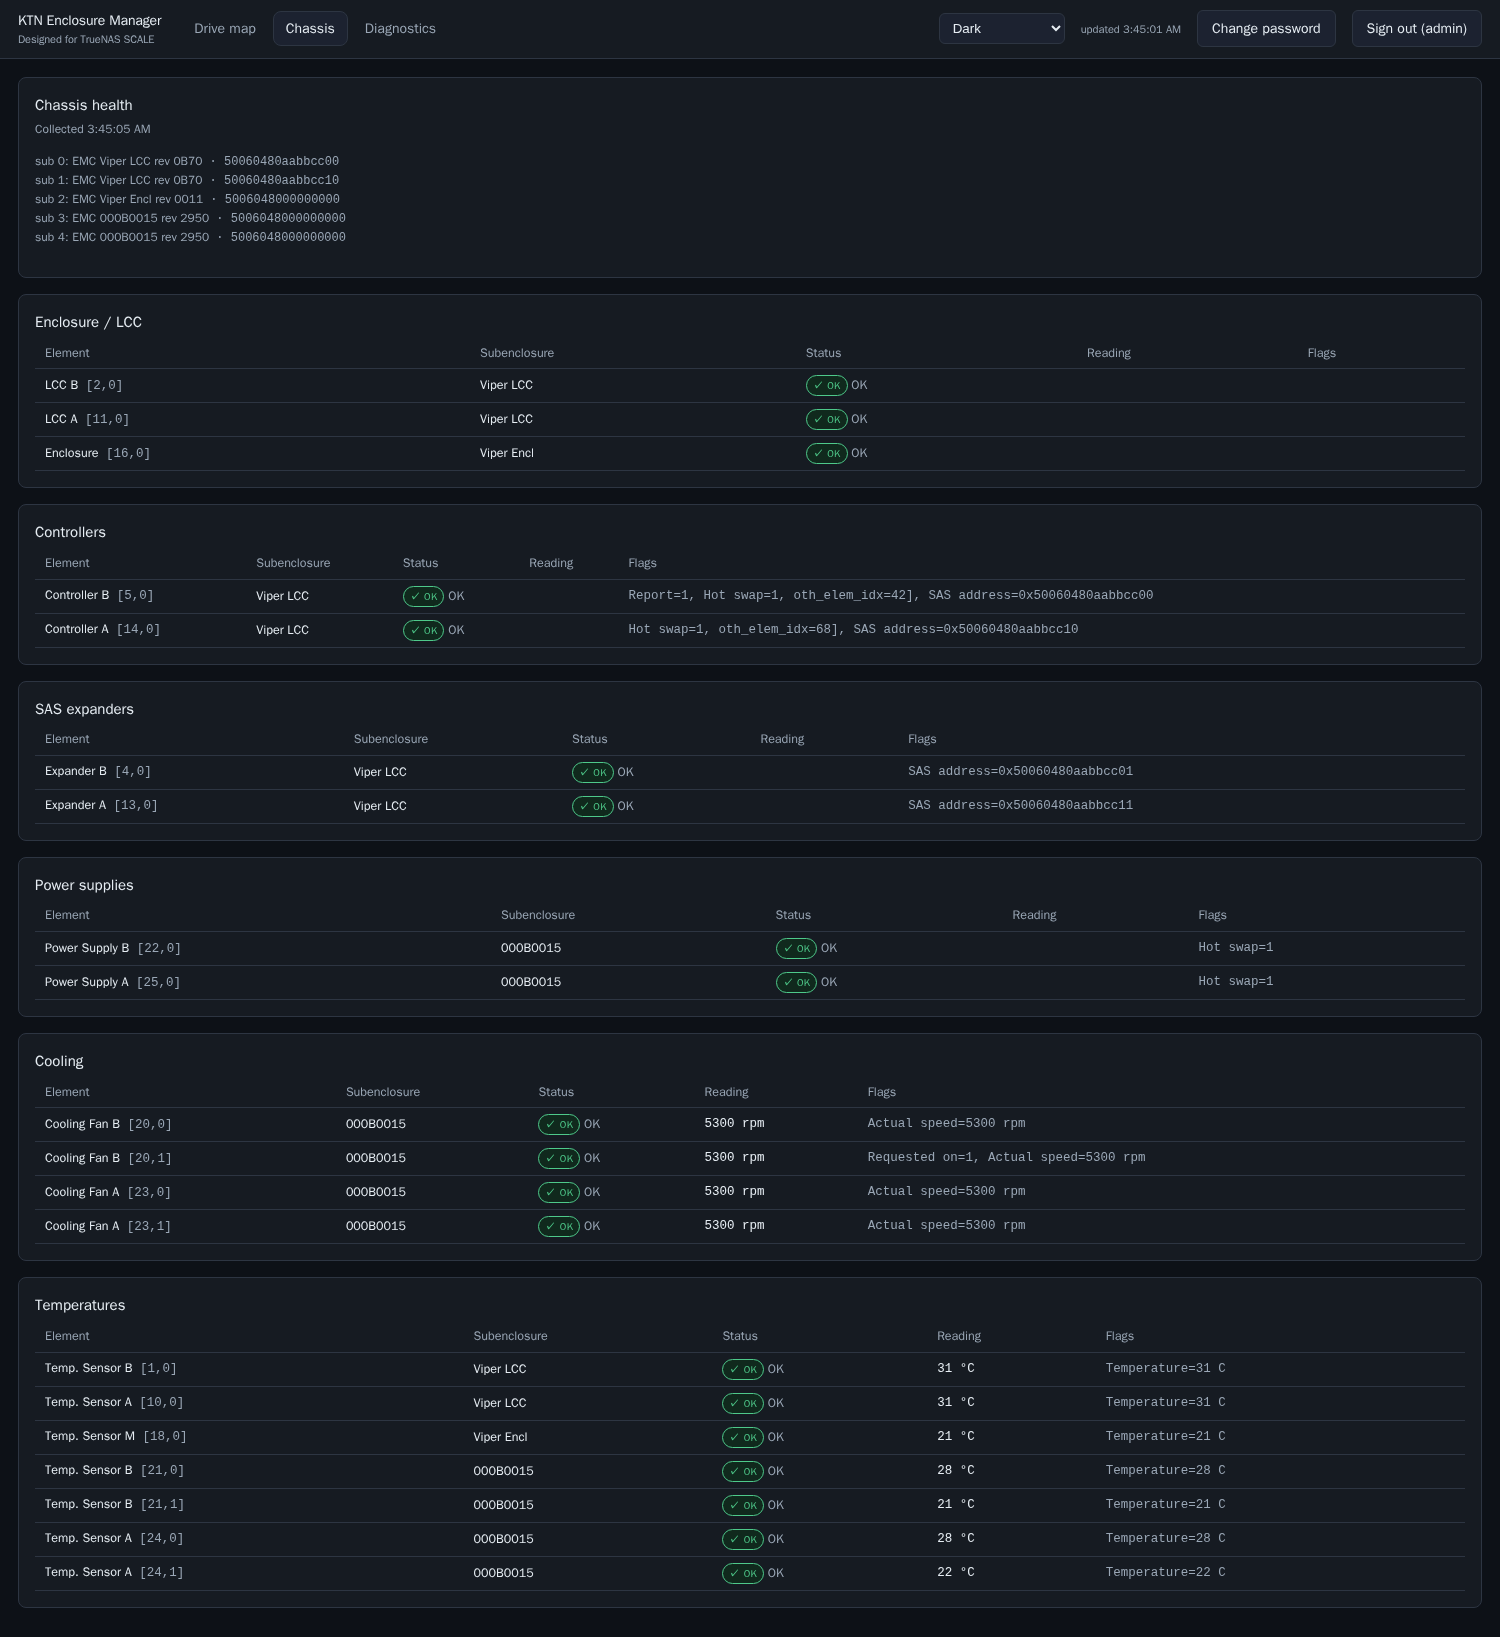
×
![Full Screenshot]()
Security Capabilities
- KTN Enclosure Manager is able to change group ID of processes
- KTN Enclosure Manager is able to change user ID of processes
App Metadata (Raw File)
{
"1.0.1": {
"healthy": true,
"supported": true,
"healthy_error": null,
"location": "/__w/apps/apps/trains/community/ktn-enclosure-manager/1.0.1",
"last_update": "2026-11-18 09:27:01",
"required_features": [],
"human_version": "1.6.3_1.0.1",
"version": "1.0.1",
"app_metadata": {
"app_version": "1.6.3",
"capabilities": [
{
"description": "KTN Enclosure Manager is able to change group ID of processes",
"name": "SETGID"
},
{
"description": "KTN Enclosure Manager is able to change user ID of processes",
"name": "SETUID"
}
],
"categories": [
"monitoring"
],
"changelog_url": "https://github.com/MechanicalCoderX/ktn-enclosure-manager/releases",
"date_added": "2026-11-17",
"description": "Physical drive-bay map, chassis telemetry and IDENT LED control for SES disk shelves attached to TrueNAS SCALE.",
"home": "https://github.com/MechanicalCoderX/ktn-enclosure-manager",
"host_mounts": [],
"icon": "https://media.sys.truenas.net/apps/ktn-enclosure-manager/icons/icon.svg",
"keywords": [
"enclosure",
"ses",
"sas",
"jbod",
"disk-shelf",
"identify"
],
"lib_version": "2.3.20",
"lib_version_hash": "cb54aeb50c3d06a90e5d9e80a852317db8336b4c68456aaaa6ce61fc2f8ed1dd",
"maintainers": [
{
"email": "dev@truenas.com",
"name": "truenas",
"url": "https://www.truenas.com/"
}
],
"name": "ktn-enclosure-manager",
"run_as_context": [
{
"description": "Container [ktn-enclosure-manager] runs as root user and group.",
"gid": 0,
"group_name": "Host group is [root]",
"uid": 0,
"user_name": "Host user is [root]"
}
],
"screenshots": [
"https://media.sys.truenas.net/apps/ktn-enclosure-manager/screenshots/screenshot1.png",
"https://media.sys.truenas.net/apps/ktn-enclosure-manager/screenshots/screenshot2.png",
"https://media.sys.truenas.net/apps/ktn-enclosure-manager/screenshots/screenshot3.png"
],
"sources": [
"https://apps.truenas.com/catalog/ktn-enclosure-manager_community/",
"https://github.com/MechanicalCoderX/ktn-enclosure-manager"
],
"title": "KTN Enclosure Manager",
"train": "community",
"version": "1.0.1"
},
"schema": {
"groups": [
{
"name": "KTN Enclosure Manager Configuration",
"description": "Configure KTN Enclosure Manager"
},
{
"name": "Network Configuration",
"description": "Configure Network for KTN Enclosure Manager"
},
{
"name": "Storage Configuration",
"description": "Configure Storage for KTN Enclosure Manager"
},
{
"name": "Labels Configuration",
"description": "Configure Labels for KTN Enclosure Manager"
},
{
"name": "Resources Configuration",
"description": "Configure Resources for KTN Enclosure Manager"
}
],
"questions": [
{
"variable": "TZ",
"group": "KTN Enclosure Manager Configuration",
"label": "Timezone",
"schema": {
"type": "string",
"default": "Etc/UTC",
"required": true,
"$ref": [
"definitions/timezone"
]
}
},
{
"variable": "ktn",
"label": "",
"group": "KTN Enclosure Manager Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "devices",
"label": "Devices",
"description": "The SCSI generic device nodes for your enclosures.</br>\nFind them with: lsscsi -g | grep enclosu</br>\nEg: Host Device: /dev/sg16, Container Device: /dev/sg16\n",
"schema": {
"type": "list",
"min": 1,
"required": true,
"default": [],
"items": [
{
"variable": "device",
"label": "Device",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "host_device",
"label": "Host Device",
"description": "The device node on the host.",
"schema": {
"type": "string",
"required": true,
"valid_chars": "^/dev/(sg|bsg)[a-zA-Z0-9/:]+$",
"valid_chars_error": "Must be a /dev/sg* or /dev/bsg/* path"
}
},
{
"variable": "container_device",
"label": "Container Device",
"description": "The device node inside the container. Normally the same as the host device.",
"schema": {
"type": "string",
"required": true,
"valid_chars": "^/dev/(sg|bsg)[a-zA-Z0-9/:]+$",
"valid_chars_error": "Must be a /dev/sg* or /dev/bsg/* path"
}
}
]
}
}
]
}
},
{
"variable": "allowlist",
"label": "Restrict to Enclosure IDs",
"description": "The enclosure logical identifiers to manage.</br>\nLeave empty to manage every enclosure found.</br>\nFind yours with: cat /sys/class/enclosure/*/id\n",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "enclosure_id",
"label": "Enclosure ID",
"schema": {
"type": "string",
"default": "",
"required": true
}
}
]
}
},
{
"variable": "auth_required",
"label": "Require a login",
"description": "Require an account to view the dashboard.</br>\nWhen enabled, you create an administrator on first run.</br>\nWhen disabled, anyone who can reach the port can read everything the\napp can read, including the audit log and raw sg_ses output.\n",
"schema": {
"type": "boolean",
"default": true
}
},
{
"variable": "allow_anonymous_ident",
"label": "Allow Identify without a login",
"description": "Allow the Identify LED to be set without an account.</br>\nOnly applies when Require a login is disabled.\n",
"schema": {
"type": "boolean",
"default": false,
"show_if": [
[
"auth_required",
"=",
false
]
]
}
},
{
"variable": "truenas_api_key",
"label": "TrueNAS API Key",
"description": "Used for pool, vdev, ZFS error and SMART data.</br>\nLeave empty to run without it. The drive map, chassis telemetry and\nIdentify all work without it.</br>\nCreate one under <b>Credentials -> Users</b>: open the user and choose <b>Access -> View API Keys</b>\nand add a key, for a user with the <b>Readonly Admin</b> role.\n",
"schema": {
"type": "string",
"default": "",
"private": true
}
},
{
"variable": "truenas_port",
"label": "TrueNAS Web Interface HTTPS Port",
"description": "The HTTPS port of the TrueNAS web interface (System > General Settings > GUI).",
"schema": {
"type": "int",
"default": 443,
"min": 1,
"max": 65535,
"required": true,
"show_if": [
[
"truenas_api_key",
"!=",
""
]
]
}
},
{
"variable": "additional_envs",
"label": "Additional Environment Variables",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "env",
"label": "Environment Variable",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Name",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "value",
"label": "Value",
"schema": {
"type": "string"
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "network",
"label": "",
"group": "Network Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "web_port",
"label": "WebUI Port",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "bind_mode",
"label": "Port Bind Mode",
"description": "The port bind mode.</br>\n- Publish: The port will be published on the host for external access.</br>\n- Expose: The port will be exposed for inter-container communication.</br>\n- None: The port will not be exposed or published.</br>\nNote: If the Dockerfile defines an EXPOSE directive,\nthe port will still be exposed for inter-container communication regardless of this setting.\n",
"schema": {
"type": "string",
"default": "published",
"enum": [
{
"value": "published",
"description": "Publish port on the host for external access"
},
{
"value": "exposed",
"description": "Expose port for inter-container communication"
},
{
"value": "",
"description": "None"
}
]
}
},
{
"variable": "port_number",
"label": "Port Number",
"schema": {
"type": "int",
"default": 30598,
"min": 1,
"max": 65535,
"required": true
}
},
{
"variable": "host_ips",
"label": "Host IPs",
"description": "IPs on the host to bind this port",
"schema": {
"type": "list",
"show_if": [
[
"bind_mode",
"=",
"published"
]
],
"default": [],
"items": [
{
"variable": "host_ip",
"label": "Host IP",
"schema": {
"type": "string",
"required": true,
"$ref": [
"definitions/node_bind_ip"
]
}
}
]
}
}
]
}
},
{
"variable": "networks",
"label": "Networks",
"description": "The docker networks to join",
"schema": {
"type": "list",
"show_if": [
[
"host_network",
"=",
false
]
],
"default": [],
"items": [
{
"variable": "network",
"label": "Network",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Name",
"description": "The name of the network to join.</br>\nThe network must already exist.\n",
"schema": {
"type": "string",
"default": "",
"required": true
}
},
{
"variable": "containers",
"label": "Containers",
"description": "The containers to add to this network.",
"schema": {
"type": "list",
"items": [
{
"variable": "container",
"label": "Container",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Container Name",
"schema": {
"type": "string",
"required": true,
"enum": [
{
"value": "ktn-enclosure-manager",
"description": "ktn-enclosure-manager"
}
]
}
},
{
"variable": "config",
"label": "Container Network Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "aliases",
"label": "Aliases (Optional)",
"description": "The network aliases to use for this container on this network.",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "alias",
"label": "Alias",
"schema": {
"type": "string"
}
}
]
}
},
{
"variable": "interface_name",
"label": "Interface Name (Optional)",
"description": "The network interface name to use for this network",
"schema": {
"type": "string"
}
},
{
"variable": "mac_address",
"label": "MAC Address (Optional)",
"description": "The MAC address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "ipv4_address",
"label": "IPv4 Address (Optional)",
"description": "The IPv4 address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "ipv6_address",
"label": "IPv6 Address (Optional)",
"description": "The IPv6 address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "gw_priority",
"label": "Gateway Priority (Optional)",
"description": "Indicates the priority of the gateway for this network interface.",
"schema": {
"type": "int",
"null": true
}
},
{
"variable": "priority",
"label": "Priority (Optional)",
"description": "Indicates in which order Compose connects the service\u2019s containers to its networks.",
"schema": {
"type": "int",
"null": true
}
}
]
}
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "host_network",
"label": "Host Network",
"description": "Bind to the host network. It's recommended to keep this disabled.\n",
"schema": {
"type": "boolean",
"default": false
}
}
]
}
},
{
"variable": "storage",
"label": "",
"group": "Storage Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "data",
"label": "Data Storage",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "type",
"label": "Type",
"description": "ixVolume: Is dataset created automatically by the system.</br>\nHost Path: Is a path that already exists on the system.\n",
"schema": {
"type": "string",
"required": true,
"default": "ix_volume",
"enum": [
{
"value": "host_path",
"description": "Host Path (Path that already exists on the system)"
},
{
"value": "ix_volume",
"description": "ixVolume (Dataset created automatically by the system)"
}
]
}
},
{
"variable": "ix_volume_config",
"label": "ixVolume Configuration",
"description": "The configuration for the ixVolume dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"ix_volume"
]
],
"$ref": [
"normalize/ix_volume"
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "dataset_name",
"label": "Dataset Name",
"description": "The name of the dataset to use for storage.",
"schema": {
"type": "string",
"required": true,
"hidden": true,
"default": "data"
}
},
{
"variable": "acl_entries",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": []
}
}
]
}
},
{
"variable": "host_path_config",
"label": "Host Path Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"host_path"
]
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "acl",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
},
{
"variable": "path",
"label": "Host Path",
"description": "The host path to use for storage.",
"schema": {
"type": "hostpath",
"show_if": [
[
"acl_enable",
"=",
false
]
],
"required": true
}
}
]
}
}
]
}
},
{
"variable": "additional_storage",
"label": "Additional Storage",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "storageEntry",
"label": "Storage Entry",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "type",
"label": "Type",
"description": "ixVolume: Is dataset created automatically by the system.</br>\nHost Path: Is a path that already exists on the system.</br>\nSMB Share: Is a SMB share that is mounted to as a volume.</br>\nNFS Share: Is a NFS share that is mounted to as a volume.\n",
"schema": {
"type": "string",
"required": true,
"default": "ix_volume",
"enum": [
{
"value": "host_path",
"description": "Host Path (Path that already exists on the system)"
},
{
"value": "ix_volume",
"description": "ixVolume (Dataset created automatically by the system)"
},
{
"value": "cifs",
"description": "SMB/CIFS Share (Mounts a volume to a SMB share)"
},
{
"value": "nfs",
"description": "NFS Share (Mounts a volume to a NFS share)"
}
]
}
},
{
"variable": "read_only",
"label": "Read Only",
"description": "Mount the volume as read only.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "mount_path",
"label": "Mount Path",
"description": "The path inside the container to mount the storage.",
"schema": {
"type": "path",
"required": true
}
},
{
"variable": "host_path_config",
"label": "Host Path Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"host_path"
]
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "acl",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
},
{
"variable": "path",
"label": "Host Path",
"description": "The host path to use for storage.",
"schema": {
"type": "hostpath",
"show_if": [
[
"acl_enable",
"=",
false
]
],
"required": true
}
}
]
}
},
{
"variable": "ix_volume_config",
"label": "ixVolume Configuration",
"description": "The configuration for the ixVolume dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"ix_volume"
]
],
"$ref": [
"normalize/ix_volume"
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "dataset_name",
"label": "Dataset Name",
"description": "The name of the dataset to use for storage.",
"schema": {
"type": "string",
"required": true,
"default": "storage_entry"
}
},
{
"variable": "acl_entries",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
}
]
}
},
{
"variable": "cifs_config",
"label": "SMB Configuration",
"description": "The configuration for the SMB dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"cifs"
]
],
"attrs": [
{
"variable": "server",
"label": "Server",
"description": "The server to mount the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "path",
"label": "Path",
"description": "The path to mount the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "username",
"label": "Username",
"description": "The username to use for the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "password",
"label": "Password",
"description": "The password to use for the SMB share.",
"schema": {
"type": "string",
"required": true,
"private": true
}
},
{
"variable": "domain",
"label": "Domain",
"description": "The domain to use for the SMB share.",
"schema": {
"type": "string"
}
}
]
}
},
{
"variable": "nfs_config",
"label": "NFS Configuration",
"description": "The configuration for the NFS dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"nfs"
]
],
"attrs": [
{
"variable": "server",
"label": "Server",
"description": "The server to mount the NFS share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "path",
"label": "Path",
"description": "The path to mount the NFS share.",
"schema": {
"type": "string",
"required": true
}
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "labels",
"label": "",
"group": "Labels Configuration",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "label",
"label": "Label",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "key",
"label": "Key",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "value",
"label": "Value",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "containers",
"label": "Containers",
"description": "Containers where the label should be applied",
"schema": {
"type": "list",
"items": [
{
"variable": "container",
"label": "Container",
"schema": {
"type": "string",
"required": true,
"enum": [
{
"value": "ktn-enclosure-manager",
"description": "ktn-enclosure-manager"
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "resources",
"label": "",
"group": "Resources Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "limits",
"label": "Limits",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "cpus",
"label": "CPUs",
"description": "CPUs limit for KTN Enclosure Manager.",
"schema": {
"type": "int",
"default": 2,
"required": true
}
},
{
"variable": "memory",
"label": "Memory (in MB)",
"description": "Memory limit for KTN Enclosure Manager.",
"schema": {
"type": "int",
"default": 4096,
"required": true
}
}
]
}
}
]
}
}
]
},
"readme": "<h1>KTN Enclosure Manager</h1> <p><a href=\"https://github.com/MechanicalCoderX/ktn-enclosure-manager\">KTN Enclosure Manager</a> is a drive-bay map, chassis telemetry and IDENT LED control panel for SES disk shelves attached to TrueNAS SCALE. TrueNAS gates its built-in enclosure UI behind iX hardware, so a third-party shelf reports \"Enclosure Unavailable\"; this fills that gap without patching middleware. Telemetry uses read-only device opens, and the only write it can perform is lighting a drive bay's Identify LED.</p> <!-- x-readme:warnings:start --> <p>\u26a0\ufe0f <strong>WARNING:</strong> This app requires a TrueNAS API key, which gives it administrative control over the system.</p> <p>Misconfiguration or a malicious update can compromise data integrity, security, or system stability. Install at your own risk.</p> <!-- x-readme:warnings:end -->",
"changelog": null,
"chart_metadata": {
"app_version": "1.6.3",
"capabilities": [
{
"description": "KTN Enclosure Manager is able to change group ID of processes",
"name": "SETGID"
},
{
"description": "KTN Enclosure Manager is able to change user ID of processes",
"name": "SETUID"
}
],
"categories": [
"monitoring"
],
"changelog_url": "https://github.com/MechanicalCoderX/ktn-enclosure-manager/releases",
"date_added": "2026-11-17",
"description": "Physical drive-bay map, chassis telemetry and IDENT LED control for SES disk shelves attached to TrueNAS SCALE.",
"home": "https://github.com/MechanicalCoderX/ktn-enclosure-manager",
"host_mounts": [],
"icon": "https://media.sys.truenas.net/apps/ktn-enclosure-manager/icons/icon.svg",
"keywords": [
"enclosure",
"ses",
"sas",
"jbod",
"disk-shelf",
"identify"
],
"lib_version": "2.3.20",
"lib_version_hash": "cb54aeb50c3d06a90e5d9e80a852317db8336b4c68456aaaa6ce61fc2f8ed1dd",
"maintainers": [
{
"email": "dev@truenas.com",
"name": "truenas",
"url": "https://www.truenas.com/"
}
],
"name": "ktn-enclosure-manager",
"run_as_context": [
{
"description": "Container [ktn-enclosure-manager] runs as root user and group.",
"gid": 0,
"group_name": "Host group is [root]",
"uid": 0,
"user_name": "Host user is [root]"
}
],
"screenshots": [
"https://media.sys.truenas.net/apps/ktn-enclosure-manager/screenshots/screenshot1.png",
"https://media.sys.truenas.net/apps/ktn-enclosure-manager/screenshots/screenshot2.png",
"https://media.sys.truenas.net/apps/ktn-enclosure-manager/screenshots/screenshot3.png"
],
"sources": [
"https://apps.truenas.com/catalog/ktn-enclosure-manager_community/",
"https://github.com/MechanicalCoderX/ktn-enclosure-manager"
],
"title": "KTN Enclosure Manager",
"train": "community",
"version": "1.0.1"
}
}
}Support, maintenance, and documentation for applications within the Community catalog is handled by the TrueNAS community. The TrueNAS Applications Market hosts but does not validate or maintain any linked resources associated with this app.
There currently aren’t any resources available for this application!
Please help the TrueNAS community add resources here or discuss this application in the TrueNAS Community forum.