

nexsift
Get Started with Apps!
Keywords: notifications, alerts, gotify, ntfy, syslog, homelab
Train: Community
Home Page: https://github.com/DerKezorm/nexsift
Added: 2026-10-02
Last Updated: 2026-10-02
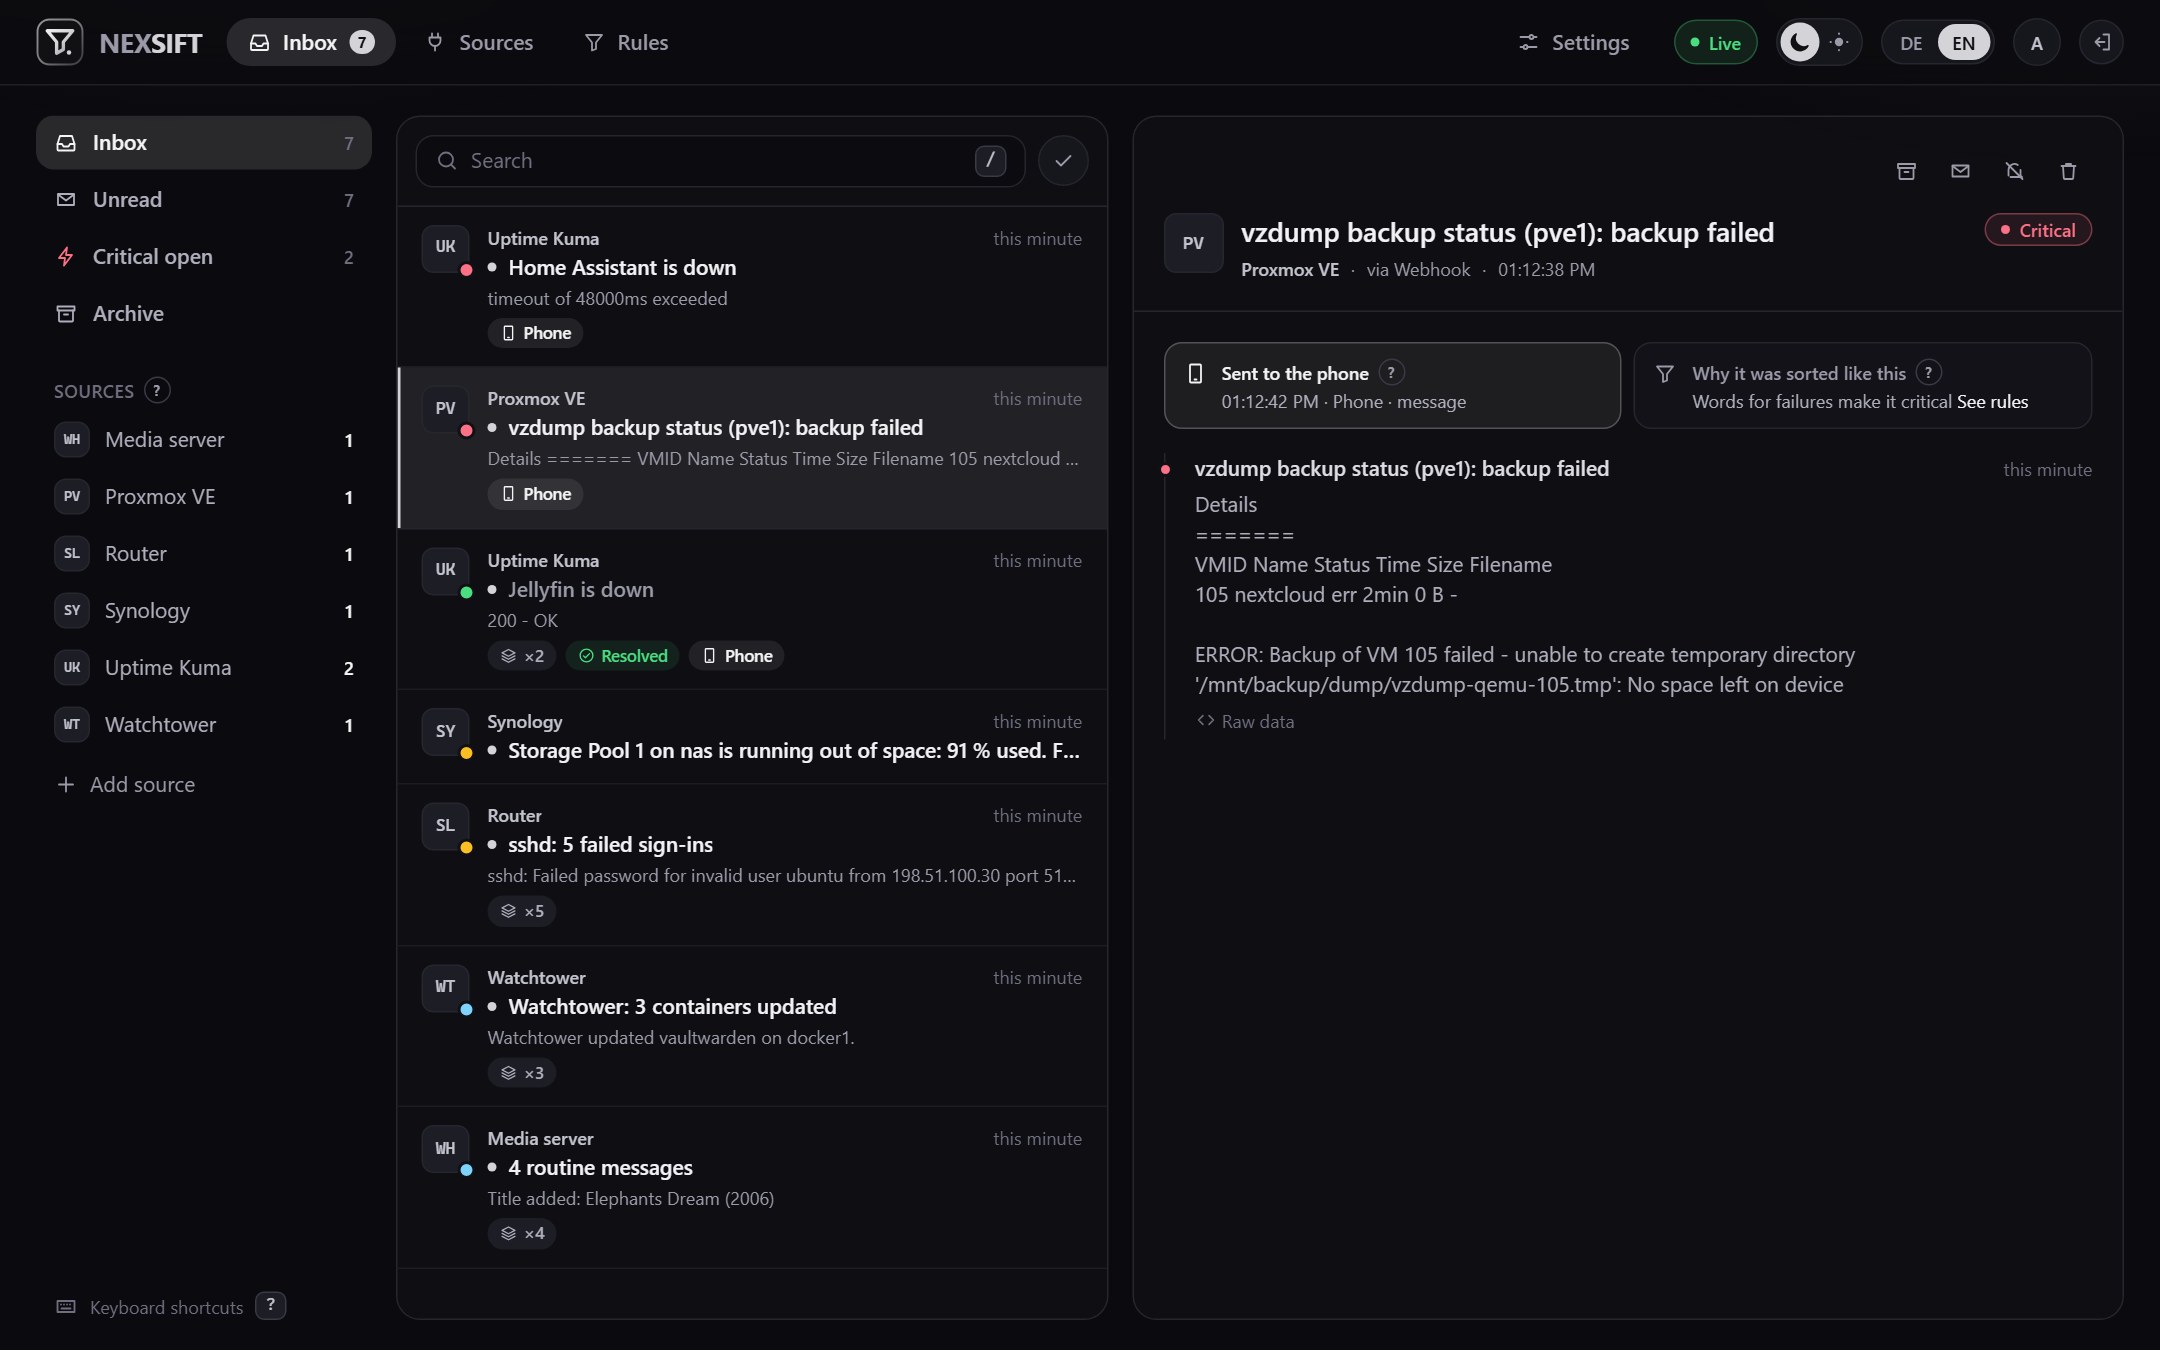
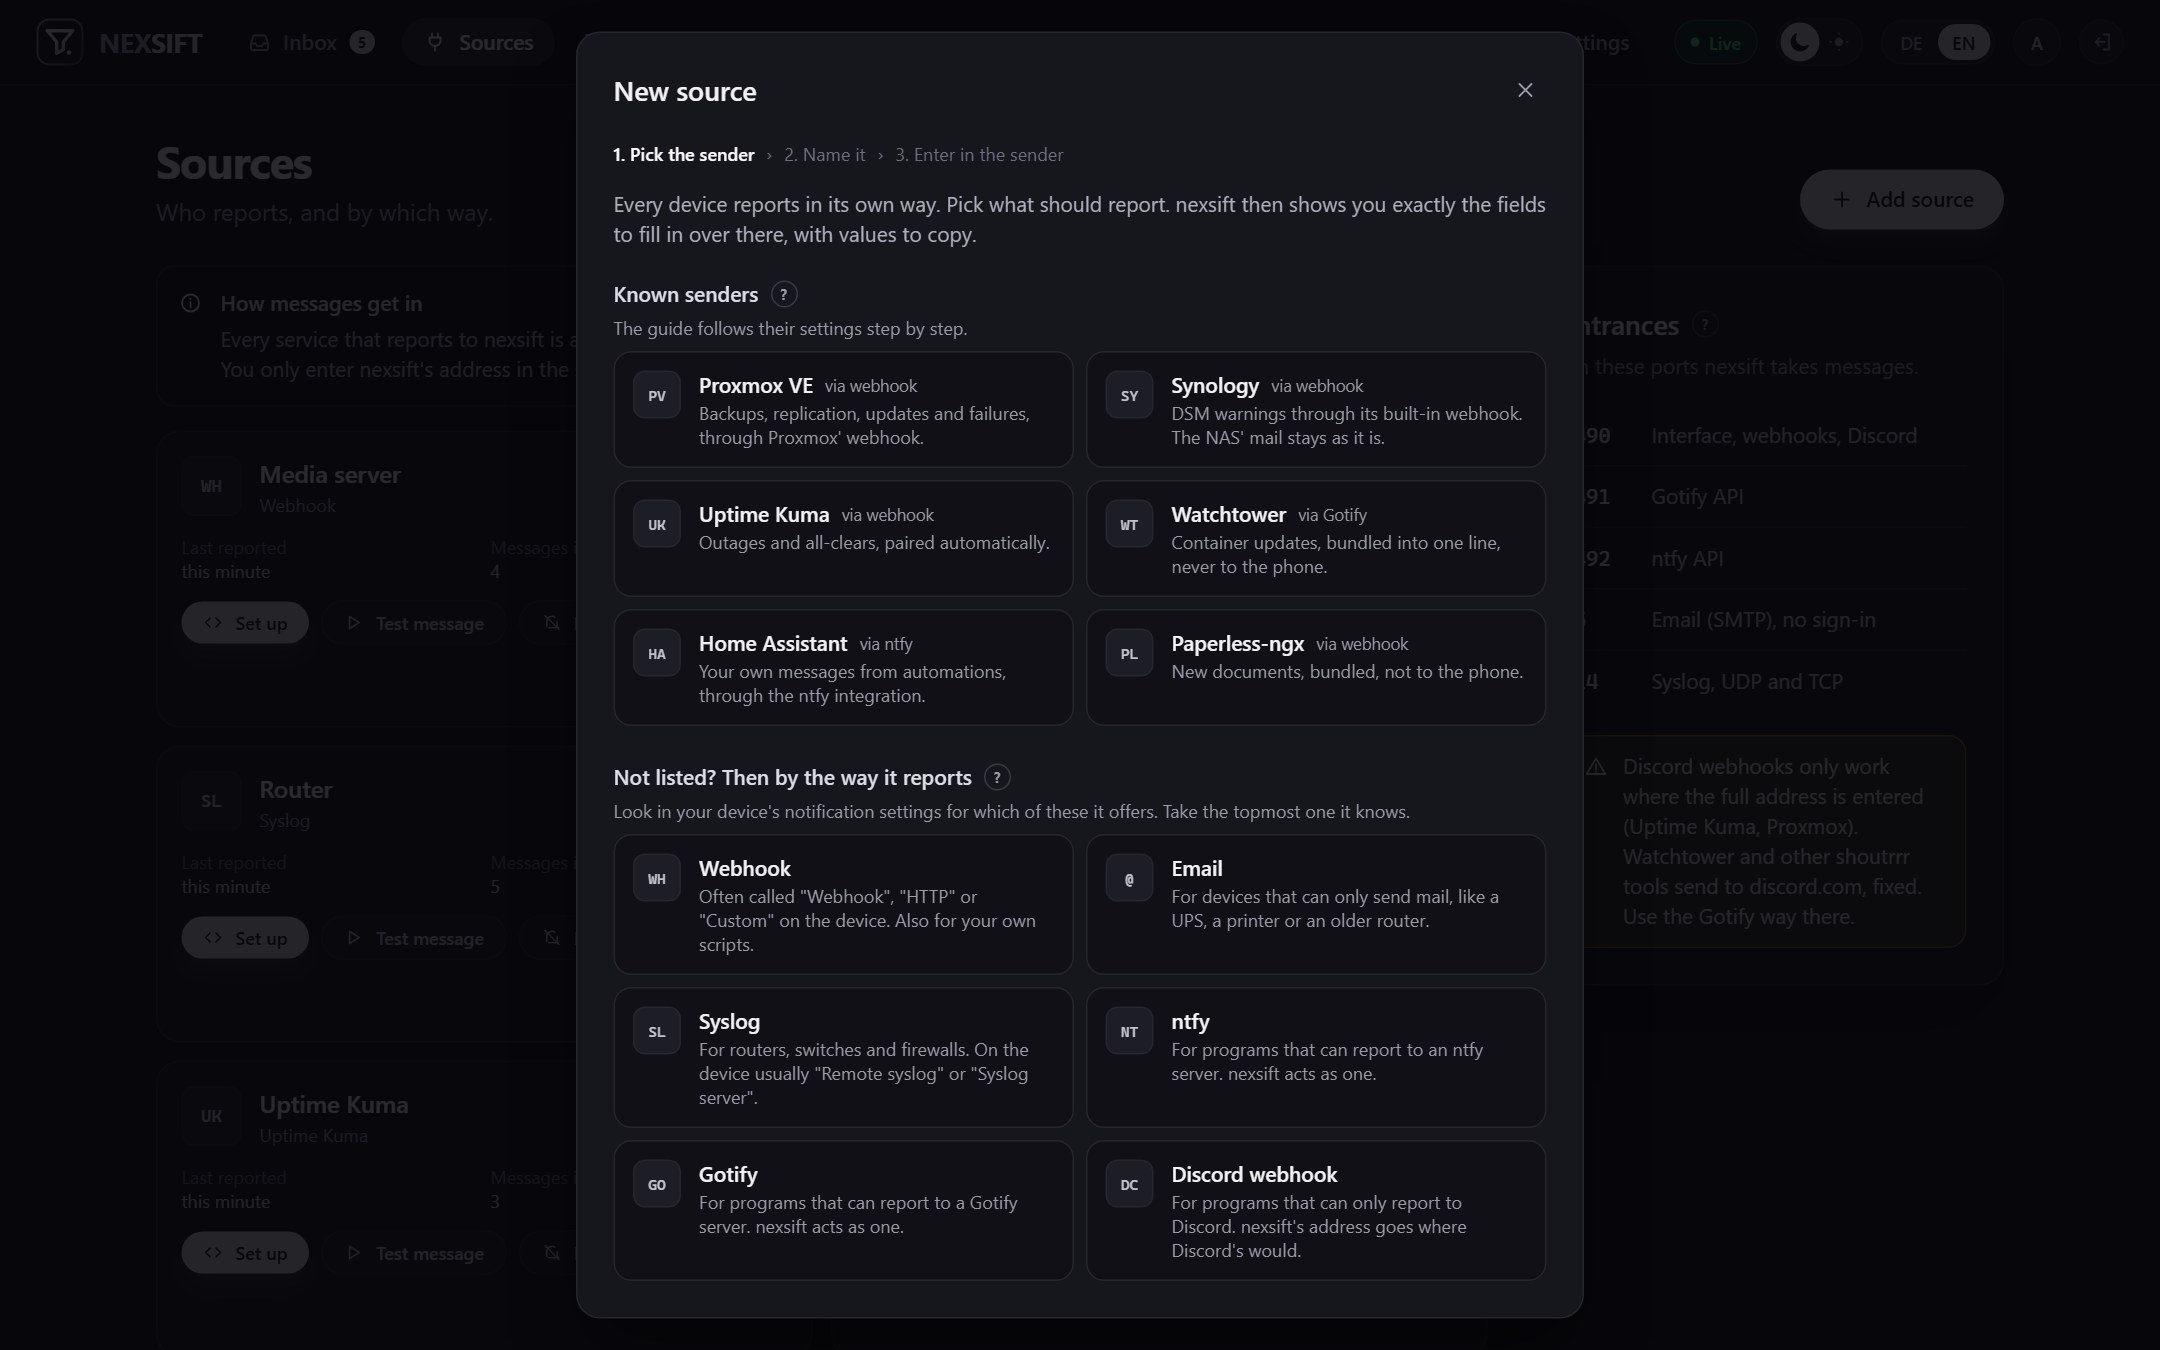
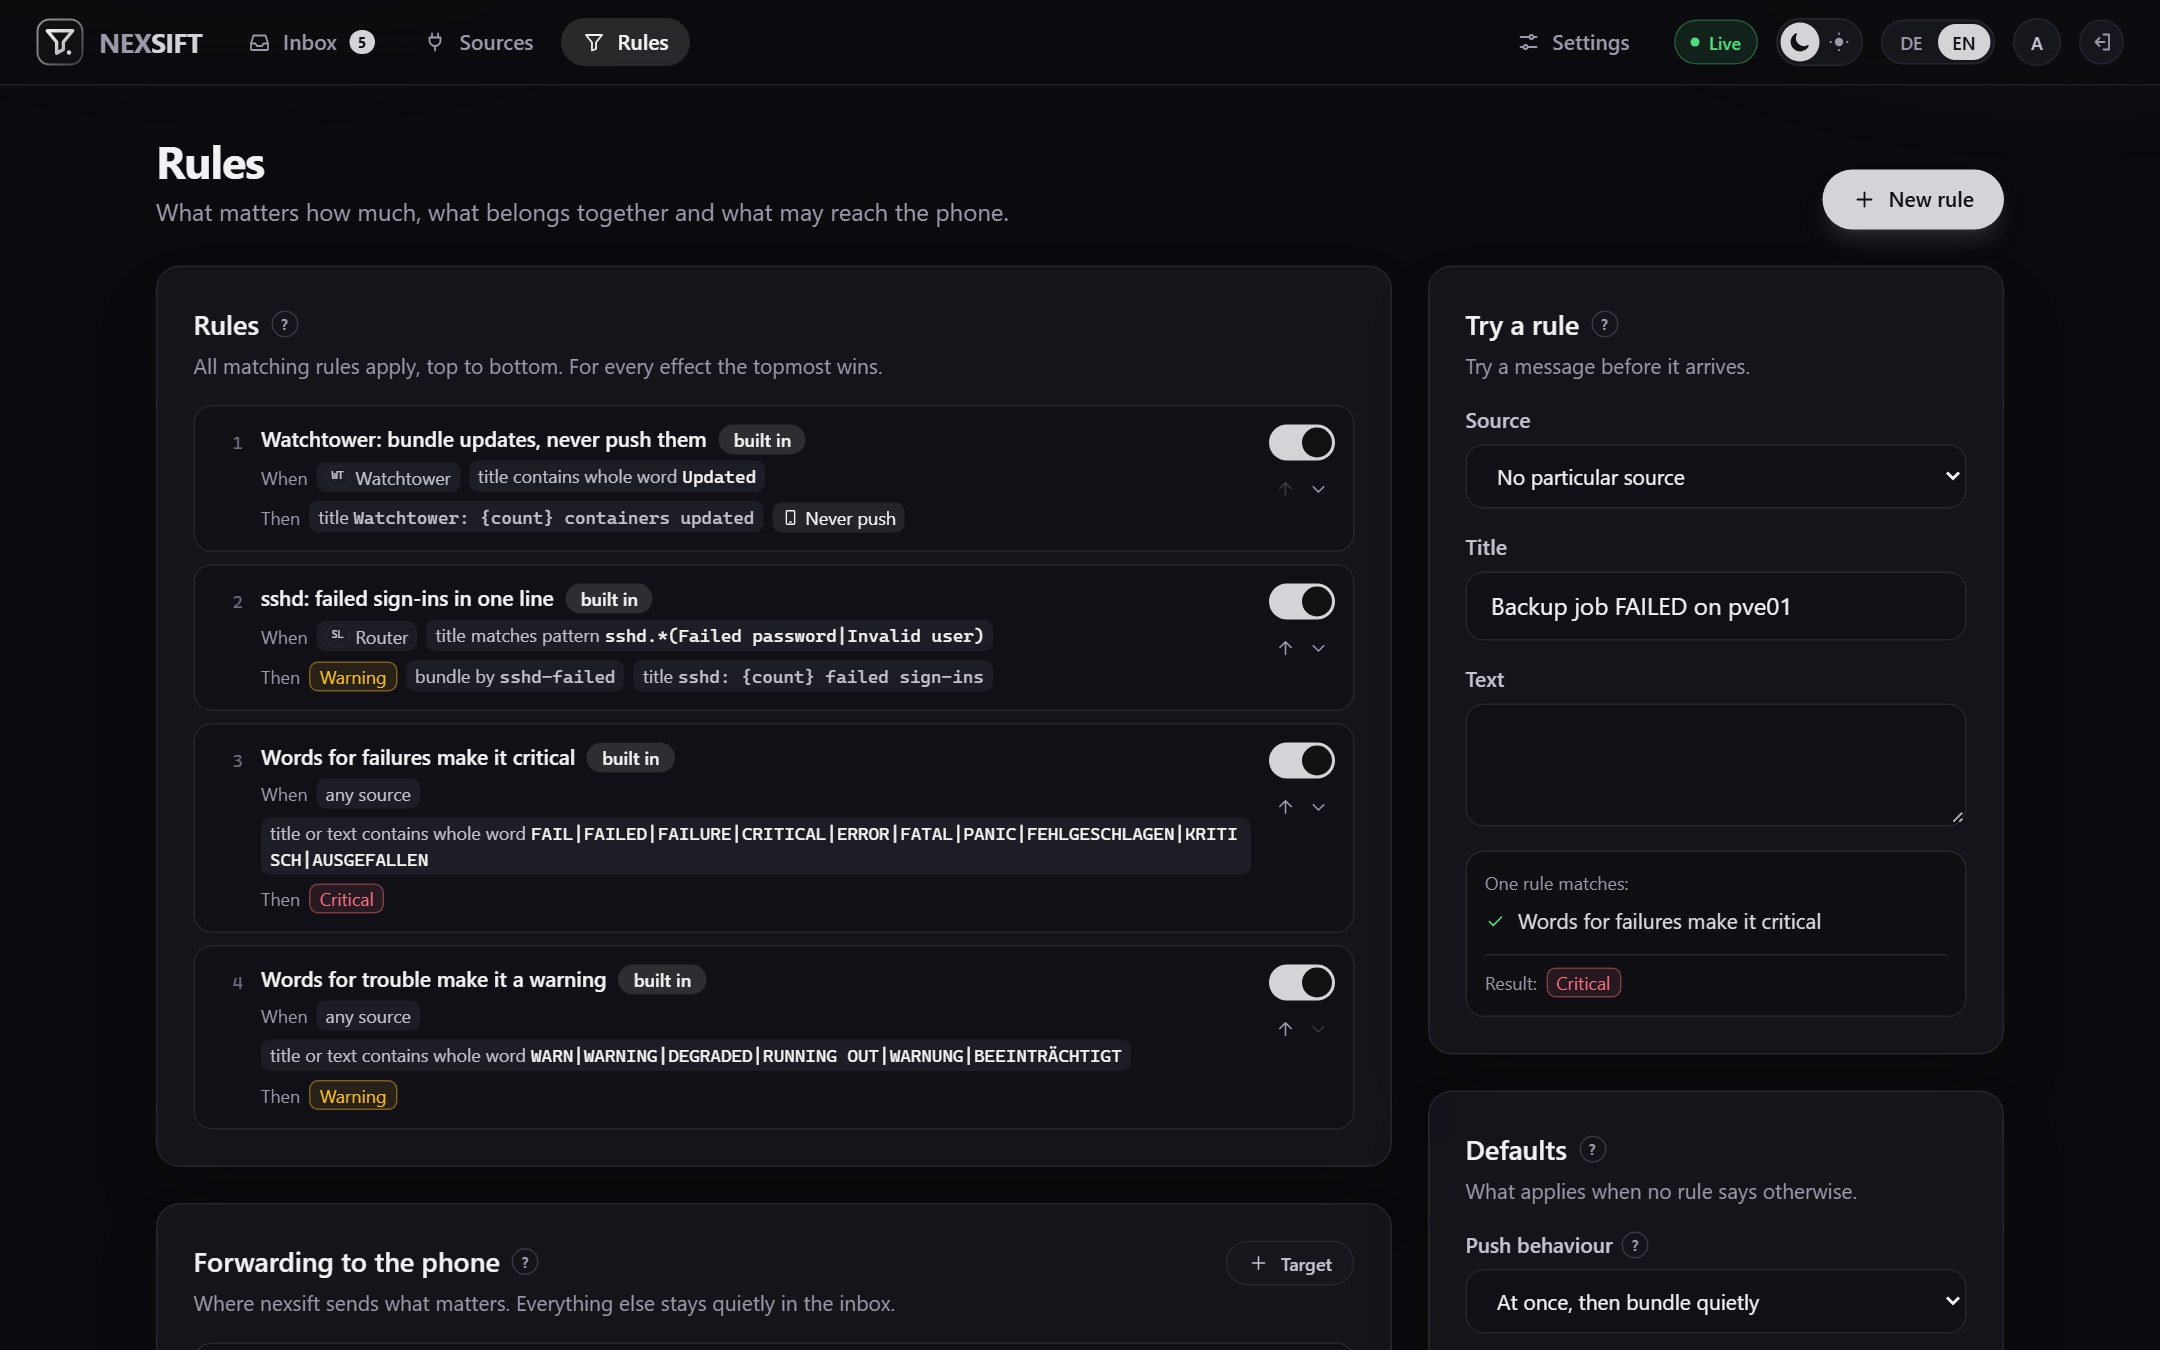
The filter for your homelab's notifications. Services report to nexsift instead of to your phone, through doors that answer like Gotify, ntfy, a Discord webhook, SMTP or syslog. nexsift sorts everything into one inbox, bundles the routine and passes on only what matters, through ntfy, Gotify, Telegram, Apprise, a webhook or Web Push.
Run as Context- Container [nexsift] can run as any non-root user and group.
Group: 568 / Host group is [apps]
User: 568 / Host user is [apps]
App Metadata (Raw File)
{
"1.0.0": {
"healthy": true,
"supported": true,
"healthy_error": null,
"location": "/__w/apps/apps/trains/community/nexsift/1.0.0",
"last_update": "2026-10-02 15:56:53",
"required_features": [],
"human_version": "0.5.0_1.0.0",
"version": "1.0.0",
"app_metadata": {
"app_version": "0.5.0",
"capabilities": [],
"categories": [
"productivity"
],
"changelog_url": "https://github.com/DerKezorm/nexsift/releases",
"date_added": "2026-10-02",
"description": "The filter for your homelab's notifications. Services report to nexsift instead of to your phone, through doors that answer like Gotify, ntfy, a Discord webhook, SMTP or syslog. nexsift sorts everything into one inbox, bundles the routine and passes on only what matters, through ntfy, Gotify, Telegram, Apprise, a webhook or Web Push.",
"home": "https://github.com/DerKezorm/nexsift",
"host_mounts": [],
"icon": "https://media.sys.truenas.net/apps/nexsift/icons/icon.png",
"keywords": [
"notifications",
"alerts",
"gotify",
"ntfy",
"syslog",
"homelab"
],
"lib_version": "2.3.15",
"lib_version_hash": "418b1697e018a564438ced4d735f4ced3ea16cc9fa74971a6040e769c80a66e5",
"maintainers": [
{
"email": "dev@truenas.com",
"name": "truenas",
"url": "https://www.truenas.com/"
}
],
"name": "nexsift",
"run_as_context": [
{
"description": "Container [nexsift] can run as any non-root user and group.",
"gid": 568,
"group_name": "Host group is [apps]",
"uid": 568,
"user_name": "Host user is [apps]"
}
],
"screenshots": [
"https://media.sys.truenas.net/apps/nexsift/screenshots/screenshot1.jpg",
"https://media.sys.truenas.net/apps/nexsift/screenshots/screenshot2.jpg",
"https://media.sys.truenas.net/apps/nexsift/screenshots/screenshot3.jpg"
],
"sources": [
"https://apps.truenas.com/catalog/nexsift_community/",
"https://github.com/DerKezorm/nexsift"
],
"title": "nexsift",
"train": "community",
"version": "1.0.0"
},
"schema": {
"groups": [
{
"name": "nexsift Configuration",
"description": "Configure nexsift"
},
{
"name": "User and Group Configuration",
"description": "Configure User and Group for nexsift"
},
{
"name": "Network Configuration",
"description": "Configure Network for nexsift"
},
{
"name": "Storage Configuration",
"description": "Configure Storage for nexsift"
},
{
"name": "Labels Configuration",
"description": "Configure Labels for nexsift"
},
{
"name": "Resources Configuration",
"description": "Configure Resources for nexsift"
}
],
"questions": [
{
"variable": "TZ",
"group": "nexsift Configuration",
"label": "Timezone",
"schema": {
"type": "string",
"default": "Etc/UTC",
"required": true,
"$ref": [
"definitions/timezone"
]
}
},
{
"variable": "nexsift",
"label": "",
"group": "nexsift Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "secret_key",
"label": "Secret Key",
"description": "Protects the stored secrets: source tokens, push target credentials,\nthe OpenID Connect client secret and the Web Push keys.</br>\nKeep a copy. Changing it makes these secrets unreadable, and a backup\narchive restores onto another installation only with the same key.\n",
"schema": {
"type": "string",
"default": "",
"min_length": 16,
"private": true,
"required": true
}
},
{
"variable": "additional_envs",
"label": "Additional Environment Variables",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "env",
"label": "Environment Variable",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Name",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "value",
"label": "Value",
"schema": {
"type": "string"
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "run_as",
"label": "",
"group": "User and Group Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "user",
"label": "User ID",
"description": "The user id that nexsift files will be owned by.",
"schema": {
"type": "int",
"min": 568,
"default": 568,
"required": true
}
},
{
"variable": "group",
"label": "Group ID",
"description": "The group id that nexsift files will be owned by.",
"schema": {
"type": "int",
"min": 568,
"default": 568,
"required": true
}
}
]
}
},
{
"variable": "network",
"label": "",
"group": "Network Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "web_port",
"label": "WebUI Port",
"description": "The interface, nexsift's own webhooks and Discord-style webhooks.",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "bind_mode",
"label": "Port Bind Mode",
"description": "The port bind mode.</br>\n- Publish: The port will be published on the host for external access.</br>\n- Expose: The port will be exposed for inter-container communication.</br>\n- None: The port will not be exposed or published.</br>\nNote: If the Dockerfile defines an EXPOSE directive,\nthe port will still be exposed for inter-container communication regardless of this setting.\n",
"schema": {
"type": "string",
"default": "published",
"enum": [
{
"value": "published",
"description": "Publish port on the host for external access"
},
{
"value": "exposed",
"description": "Expose port for inter-container communication"
},
{
"value": "",
"description": "None"
}
]
}
},
{
"variable": "port_number",
"label": "Port Number",
"schema": {
"type": "int",
"default": 30510,
"min": 1,
"max": 65535,
"required": true
}
},
{
"variable": "host_ips",
"label": "Host IPs",
"description": "IPs on the host to bind this port",
"schema": {
"type": "list",
"show_if": [
[
"bind_mode",
"=",
"published"
]
],
"default": [],
"items": [
{
"variable": "host_ip",
"label": "Host IP",
"schema": {
"type": "string",
"required": true,
"$ref": [
"definitions/node_bind_ip"
]
}
}
]
}
}
]
}
},
{
"variable": "gotify_port",
"label": "Gotify Port",
"description": "Answers like a Gotify server (POST /message), for Watchtower and other shoutrrr tools.",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "bind_mode",
"label": "Port Bind Mode",
"description": "The port bind mode.</br>\n- Publish: The port will be published on the host for external access.</br>\n- Expose: The port will be exposed for inter-container communication.</br>\n- None: The port will not be exposed or published.</br>\nNote: If the Dockerfile defines an EXPOSE directive,\nthe port will still be exposed for inter-container communication regardless of this setting.\n",
"schema": {
"type": "string",
"default": "published",
"enum": [
{
"value": "published",
"description": "Publish port on the host for external access"
},
{
"value": "exposed",
"description": "Expose port for inter-container communication"
},
{
"value": "",
"description": "None"
}
]
}
},
{
"variable": "port_number",
"label": "Port Number",
"schema": {
"type": "int",
"default": 30511,
"min": 1,
"max": 65535,
"required": true
}
},
{
"variable": "host_ips",
"label": "Host IPs",
"description": "IPs on the host to bind this port",
"schema": {
"type": "list",
"show_if": [
[
"bind_mode",
"=",
"published"
]
],
"default": [],
"items": [
{
"variable": "host_ip",
"label": "Host IP",
"schema": {
"type": "string",
"required": true,
"$ref": [
"definitions/node_bind_ip"
]
}
}
]
}
}
]
}
},
{
"variable": "ntfy_port",
"label": "ntfy Port",
"description": "Answers like an ntfy server (POST /topic), for example for the ntfy integration of Home Assistant.",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "bind_mode",
"label": "Port Bind Mode",
"description": "The port bind mode.</br>\n- Publish: The port will be published on the host for external access.</br>\n- Expose: The port will be exposed for inter-container communication.</br>\n- None: The port will not be exposed or published.</br>\nNote: If the Dockerfile defines an EXPOSE directive,\nthe port will still be exposed for inter-container communication regardless of this setting.\n",
"schema": {
"type": "string",
"default": "published",
"enum": [
{
"value": "published",
"description": "Publish port on the host for external access"
},
{
"value": "exposed",
"description": "Expose port for inter-container communication"
},
{
"value": "",
"description": "None"
}
]
}
},
{
"variable": "port_number",
"label": "Port Number",
"schema": {
"type": "int",
"default": 30512,
"min": 1,
"max": 65535,
"required": true
}
},
{
"variable": "host_ips",
"label": "Host IPs",
"description": "IPs on the host to bind this port",
"schema": {
"type": "list",
"show_if": [
[
"bind_mode",
"=",
"published"
]
],
"default": [],
"items": [
{
"variable": "host_ip",
"label": "Host IP",
"schema": {
"type": "string",
"required": true,
"$ref": [
"definitions/node_bind_ip"
]
}
}
]
}
}
]
}
},
{
"variable": "smtp_port",
"label": "SMTP Port",
"description": "Plain SMTP without sign-in, for devices that can only send mail.",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "bind_mode",
"label": "Port Bind Mode",
"description": "The port bind mode.</br>\n- Publish: The port will be published on the host for external access.</br>\n- Expose: The port will be exposed for inter-container communication.</br>\n- None: The port will not be exposed or published.</br>\nNote: If the Dockerfile defines an EXPOSE directive,\nthe port will still be exposed for inter-container communication regardless of this setting.\n",
"schema": {
"type": "string",
"default": "published",
"enum": [
{
"value": "published",
"description": "Publish port on the host for external access"
},
{
"value": "exposed",
"description": "Expose port for inter-container communication"
},
{
"value": "",
"description": "None"
}
]
}
},
{
"variable": "port_number",
"label": "Port Number",
"schema": {
"type": "int",
"default": 30513,
"min": 1,
"max": 65535,
"required": true
}
},
{
"variable": "host_ips",
"label": "Host IPs",
"description": "IPs on the host to bind this port",
"schema": {
"type": "list",
"show_if": [
[
"bind_mode",
"=",
"published"
]
],
"default": [],
"items": [
{
"variable": "host_ip",
"label": "Host IP",
"schema": {
"type": "string",
"required": true,
"$ref": [
"definitions/node_bind_ip"
]
}
}
]
}
}
]
}
},
{
"variable": "syslog_port",
"label": "Syslog Port",
"description": "Syslog over UDP and TCP on the same port number.",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "bind_mode",
"label": "Port Bind Mode",
"description": "The port bind mode.</br>\n- Publish: The port will be published on the host for external access.</br>\n- Expose: The port will be exposed for inter-container communication.</br>\n- None: The port will not be exposed or published.</br>\nNote: If the Dockerfile defines an EXPOSE directive,\nthe port will still be exposed for inter-container communication regardless of this setting.\n",
"schema": {
"type": "string",
"default": "published",
"enum": [
{
"value": "published",
"description": "Publish port on the host for external access"
},
{
"value": "exposed",
"description": "Expose port for inter-container communication"
},
{
"value": "",
"description": "None"
}
]
}
},
{
"variable": "port_number",
"label": "Port Number",
"schema": {
"type": "int",
"default": 30514,
"min": 1,
"max": 65535,
"required": true
}
},
{
"variable": "host_ips",
"label": "Host IPs",
"description": "IPs on the host to bind this port",
"schema": {
"type": "list",
"show_if": [
[
"bind_mode",
"=",
"published"
]
],
"default": [],
"items": [
{
"variable": "host_ip",
"label": "Host IP",
"schema": {
"type": "string",
"required": true,
"$ref": [
"definitions/node_bind_ip"
]
}
}
]
}
}
]
}
},
{
"variable": "networks",
"label": "Networks",
"description": "The docker networks to join",
"schema": {
"type": "list",
"show_if": [
[
"host_network",
"=",
false
]
],
"default": [],
"items": [
{
"variable": "network",
"label": "Network",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Name",
"description": "The name of the network to join.</br>\nThe network must already exist.\n",
"schema": {
"type": "string",
"default": "",
"required": true
}
},
{
"variable": "containers",
"label": "Containers",
"description": "The containers to add to this network.",
"schema": {
"type": "list",
"items": [
{
"variable": "container",
"label": "Container",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Container Name",
"schema": {
"type": "string",
"required": true,
"enum": [
{
"value": "nexsift",
"description": "nexsift"
}
]
}
},
{
"variable": "config",
"label": "Container Network Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "aliases",
"label": "Aliases (Optional)",
"description": "The network aliases to use for this container on this network.",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "alias",
"label": "Alias",
"schema": {
"type": "string"
}
}
]
}
},
{
"variable": "interface_name",
"label": "Interface Name (Optional)",
"description": "The network interface name to use for this network",
"schema": {
"type": "string"
}
},
{
"variable": "mac_address",
"label": "MAC Address (Optional)",
"description": "The MAC address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "ipv4_address",
"label": "IPv4 Address (Optional)",
"description": "The IPv4 address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "ipv6_address",
"label": "IPv6 Address (Optional)",
"description": "The IPv6 address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "gw_priority",
"label": "Gateway Priority (Optional)",
"description": "Indicates the priority of the gateway for this network interface.",
"schema": {
"type": "int",
"null": true
}
},
{
"variable": "priority",
"label": "Priority (Optional)",
"description": "Indicates in which order Compose connects the service\u2019s containers to its networks.",
"schema": {
"type": "int",
"null": true
}
}
]
}
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "host_network",
"label": "Host Network",
"description": "Bind to the host network. It's recommended to keep this disabled.\n",
"schema": {
"type": "boolean",
"default": false
}
}
]
}
},
{
"variable": "storage",
"label": "",
"group": "Storage Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "data",
"label": "Data Storage",
"description": "Holds the SQLite database with sources, rules, targets and messages, backups and logs.",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "type",
"label": "Type",
"description": "ixVolume: Is dataset created automatically by the system.</br>\nHost Path: Is a path that already exists on the system.\n",
"schema": {
"type": "string",
"required": true,
"default": "ix_volume",
"enum": [
{
"value": "host_path",
"description": "Host Path (Path that already exists on the system)"
},
{
"value": "ix_volume",
"description": "ixVolume (Dataset created automatically by the system)"
}
]
}
},
{
"variable": "ix_volume_config",
"label": "ixVolume Configuration",
"description": "The configuration for the ixVolume dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"ix_volume"
]
],
"$ref": [
"normalize/ix_volume"
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "dataset_name",
"label": "Dataset Name",
"description": "The name of the dataset to use for storage.",
"schema": {
"type": "string",
"required": true,
"hidden": true,
"default": "data"
}
},
{
"variable": "acl_entries",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": []
}
}
]
}
},
{
"variable": "host_path_config",
"label": "Host Path Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"host_path"
]
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "acl",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
},
{
"variable": "path",
"label": "Host Path",
"description": "The host path to use for storage.",
"schema": {
"type": "hostpath",
"show_if": [
[
"acl_enable",
"=",
false
]
],
"required": true
}
}
]
}
}
]
}
},
{
"variable": "additional_storage",
"label": "Additional Storage",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "storage_entry",
"label": "Storage Entry",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "type",
"label": "Type",
"description": "ixVolume: Is dataset created automatically by the system.</br>\nHost Path: Is a path that already exists on the system.</br>\nSMB Share: Is a SMB share that is mounted to as a volume.</br>\nNFS Share: Is a NFS share that is mounted to as a volume.\n",
"schema": {
"type": "string",
"required": true,
"default": "ix_volume",
"enum": [
{
"value": "host_path",
"description": "Host Path (Path that already exists on the system)"
},
{
"value": "ix_volume",
"description": "ixVolume (Dataset created automatically by the system)"
},
{
"value": "cifs",
"description": "SMB/CIFS Share (Mounts a volume to a SMB share)"
},
{
"value": "nfs",
"description": "NFS Share (Mounts a volume to a NFS share)"
}
]
}
},
{
"variable": "read_only",
"label": "Read Only",
"description": "Mount the volume as read only.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "mount_path",
"label": "Mount Path",
"description": "The path inside the container to mount the storage.",
"schema": {
"type": "path",
"required": true
}
},
{
"variable": "host_path_config",
"label": "Host Path Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"host_path"
]
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "acl",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
},
{
"variable": "path",
"label": "Host Path",
"description": "The host path to use for storage.",
"schema": {
"type": "hostpath",
"show_if": [
[
"acl_enable",
"=",
false
]
],
"required": true
}
}
]
}
},
{
"variable": "ix_volume_config",
"label": "ixVolume Configuration",
"description": "The configuration for the ixVolume dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"ix_volume"
]
],
"$ref": [
"normalize/ix_volume"
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "dataset_name",
"label": "Dataset Name",
"description": "The name of the dataset to use for storage.",
"schema": {
"type": "string",
"required": true,
"default": "storage_entry"
}
},
{
"variable": "acl_entries",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
}
]
}
},
{
"variable": "cifs_config",
"label": "SMB Configuration",
"description": "The configuration for the SMB dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"cifs"
]
],
"attrs": [
{
"variable": "server",
"label": "Server",
"description": "The server to mount the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "path",
"label": "Path",
"description": "The path to mount the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "username",
"label": "Username",
"description": "The username to use for the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "password",
"label": "Password",
"description": "The password to use for the SMB share.",
"schema": {
"type": "string",
"required": true,
"private": true
}
},
{
"variable": "domain",
"label": "Domain",
"description": "The domain to use for the SMB share.",
"schema": {
"type": "string"
}
}
]
}
},
{
"variable": "nfs_config",
"label": "NFS Configuration",
"description": "The configuration for the NFS dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"nfs"
]
],
"attrs": [
{
"variable": "server",
"label": "Server",
"description": "The server to mount the NFS share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "path",
"label": "Path",
"description": "The path to mount the NFS share.",
"schema": {
"type": "string",
"required": true
}
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "labels",
"label": "",
"group": "Labels Configuration",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "label",
"label": "Label",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "key",
"label": "Key",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "value",
"label": "Value",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "containers",
"label": "Containers",
"description": "Containers where the label should be applied",
"schema": {
"type": "list",
"items": [
{
"variable": "container",
"label": "Container",
"schema": {
"type": "string",
"required": true,
"enum": [
{
"value": "nexsift",
"description": "nexsift"
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "resources",
"label": "",
"group": "Resources Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "limits",
"label": "Limits",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "cpus",
"label": "CPUs",
"description": "CPUs limit for nexsift.",
"schema": {
"type": "int",
"default": 2,
"required": true
}
},
{
"variable": "memory",
"label": "Memory (in MB)",
"description": "Memory limit for nexsift.",
"schema": {
"type": "int",
"default": 4096,
"required": true
}
}
]
}
}
]
}
}
]
},
"readme": "<h1>nexsift</h1> <p><a href=\"https://github.com/DerKezorm/nexsift\">nexsift</a> is the filter for your homelab's notifications. Services report to nexsift instead of to your phone, through doors that answer like a Gotify server, an ntfy server, a Discord webhook, a mail server or a syslog server. nexsift collects everything in one inbox, bundles the routine, closes problems on their all-clear and passes on only what matters.</p>",
"changelog": null,
"chart_metadata": {
"app_version": "0.5.0",
"capabilities": [],
"categories": [
"productivity"
],
"changelog_url": "https://github.com/DerKezorm/nexsift/releases",
"date_added": "2026-10-02",
"description": "The filter for your homelab's notifications. Services report to nexsift instead of to your phone, through doors that answer like Gotify, ntfy, a Discord webhook, SMTP or syslog. nexsift sorts everything into one inbox, bundles the routine and passes on only what matters, through ntfy, Gotify, Telegram, Apprise, a webhook or Web Push.",
"home": "https://github.com/DerKezorm/nexsift",
"host_mounts": [],
"icon": "https://media.sys.truenas.net/apps/nexsift/icons/icon.png",
"keywords": [
"notifications",
"alerts",
"gotify",
"ntfy",
"syslog",
"homelab"
],
"lib_version": "2.3.15",
"lib_version_hash": "418b1697e018a564438ced4d735f4ced3ea16cc9fa74971a6040e769c80a66e5",
"maintainers": [
{
"email": "dev@truenas.com",
"name": "truenas",
"url": "https://www.truenas.com/"
}
],
"name": "nexsift",
"run_as_context": [
{
"description": "Container [nexsift] can run as any non-root user and group.",
"gid": 568,
"group_name": "Host group is [apps]",
"uid": 568,
"user_name": "Host user is [apps]"
}
],
"screenshots": [
"https://media.sys.truenas.net/apps/nexsift/screenshots/screenshot1.jpg",
"https://media.sys.truenas.net/apps/nexsift/screenshots/screenshot2.jpg",
"https://media.sys.truenas.net/apps/nexsift/screenshots/screenshot3.jpg"
],
"sources": [
"https://apps.truenas.com/catalog/nexsift_community/",
"https://github.com/DerKezorm/nexsift"
],
"title": "nexsift",
"train": "community",
"version": "1.0.0"
}
}
}Support, maintenance, and documentation for applications within the Community catalog is handled by the TrueNAS community. The TrueNAS Applications Market hosts but does not validate or maintain any linked resources associated with this app.
There currently aren’t any resources available for this application!
Please help the TrueNAS community add resources here or discuss this application in the TrueNAS Community forum.