

Scanvento

Scanvento
Get Started with Apps!
Get Started with Apps!
App Version:
0.0.16
(Changelog)
Keywords: asset, inventory, itam, cmdb, discovery, licence
Train: Community
Home Page: https://scanvento.com
Keywords: asset, inventory, itam, cmdb, discovery, licence
Train: Community
Home Page: https://scanvento.com
Scanvento Details
Added: 2026-11-13
Last Updated: 2026-11-13
Added: 2026-11-13
Last Updated: 2026-11-13
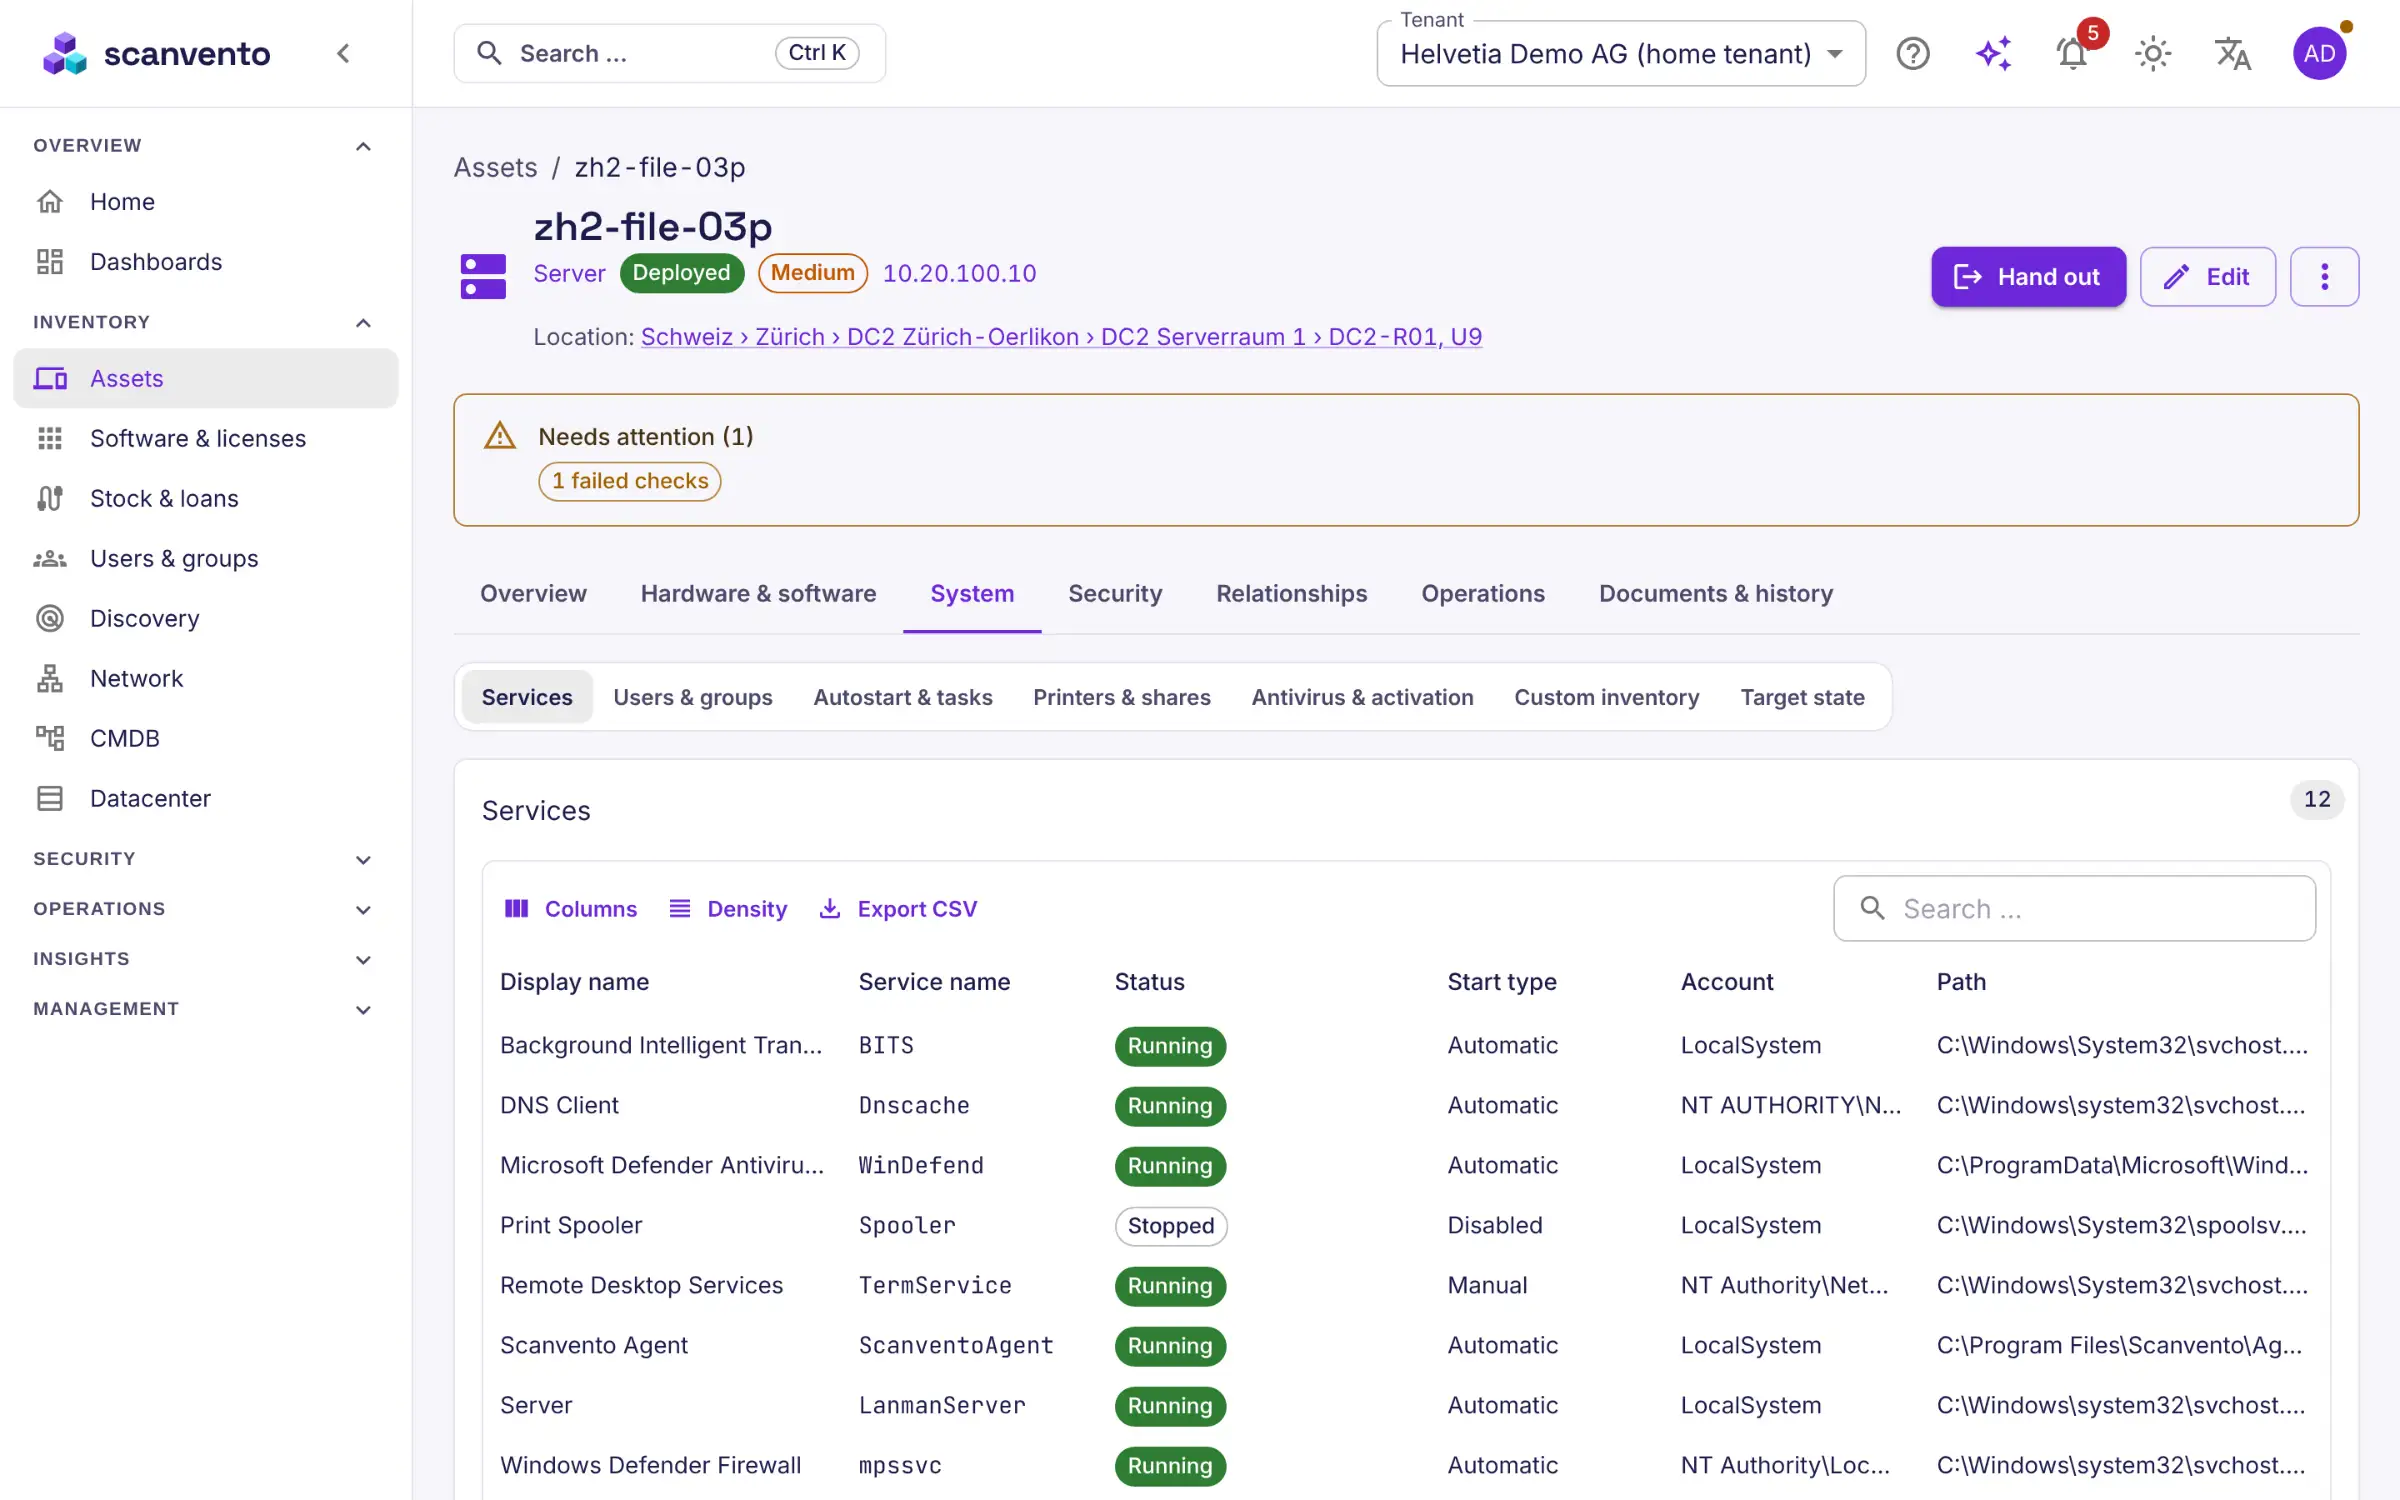
Scanvento is an IT asset management and discovery platform for hardware, software, licences, vulnerabilities and the asset lifecycle. Proprietary software, free edition up to 250 active assets without a licence file.
Run as Context- Container [postgres] runs as non-root user and group.
Group: 999 / Host group is [docker]
User: 999 / Host user is [netdata] - Container [redis] can run as any non-root user and group.
Group: 568 / Host group is [apps]
User: 568 / Host user is [apps] - Container [scanvento] can run as any non-root user and group.
Group: 568 / Host group is [apps]
User: 568 / Host user is [apps]
Screenshots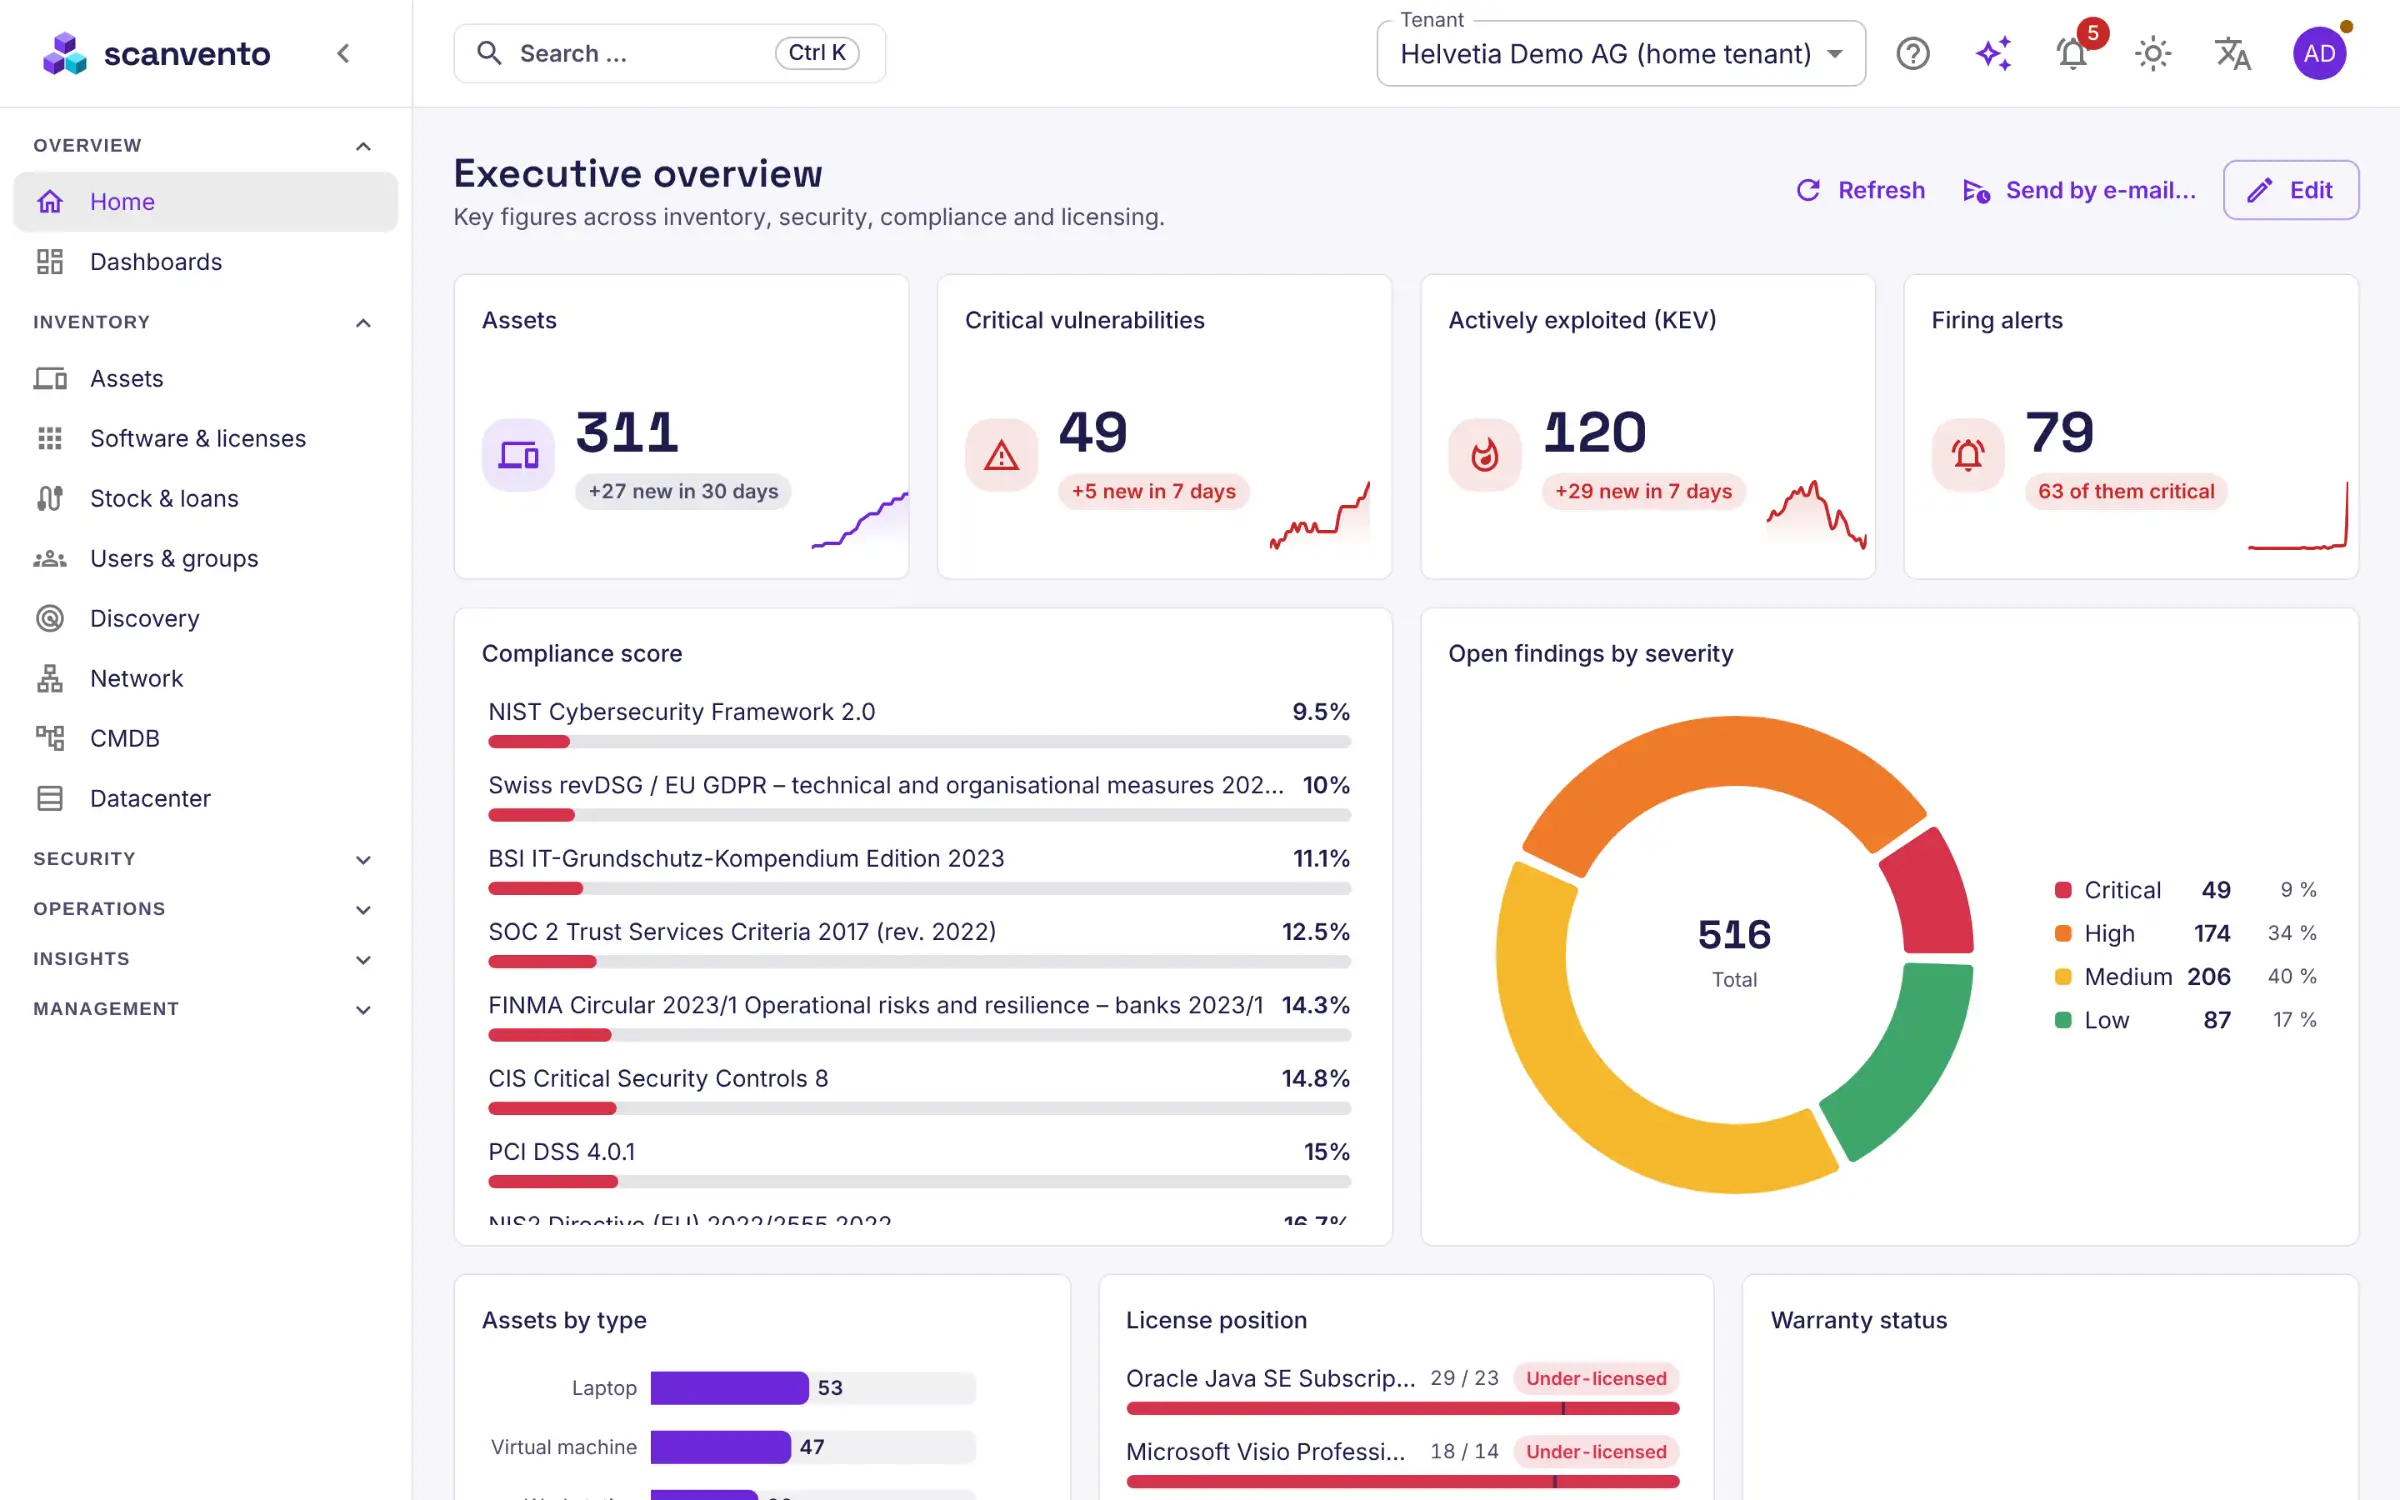
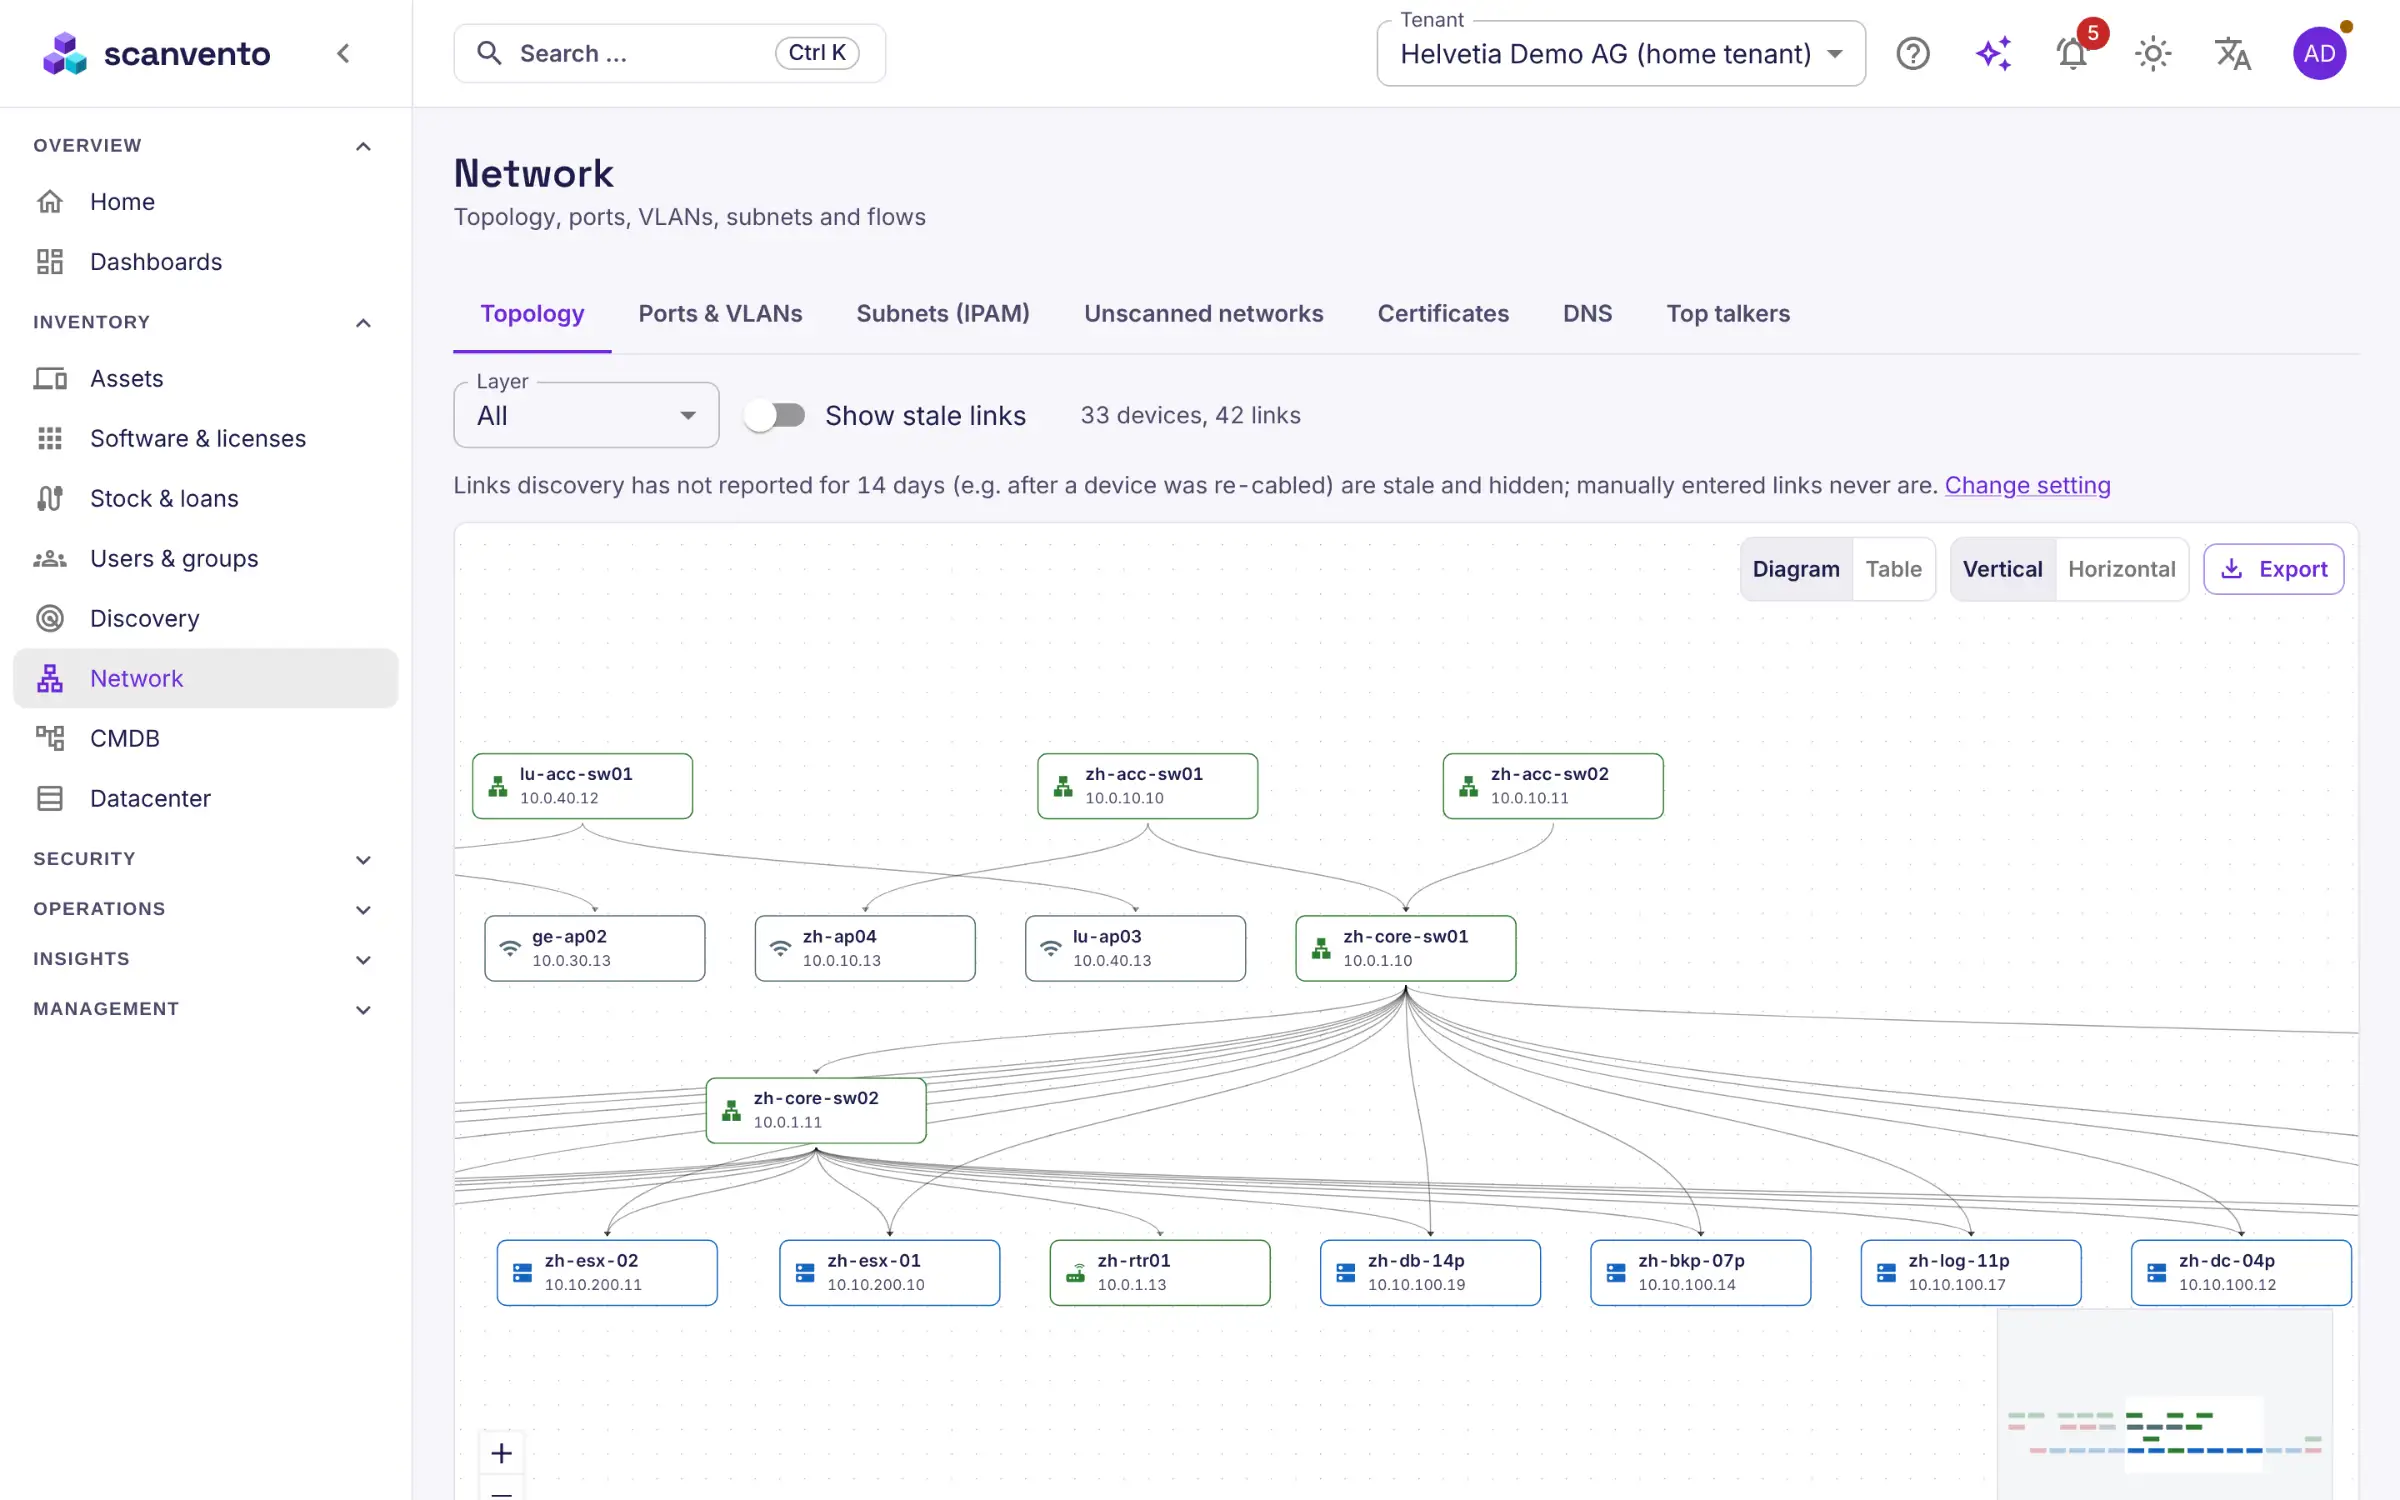
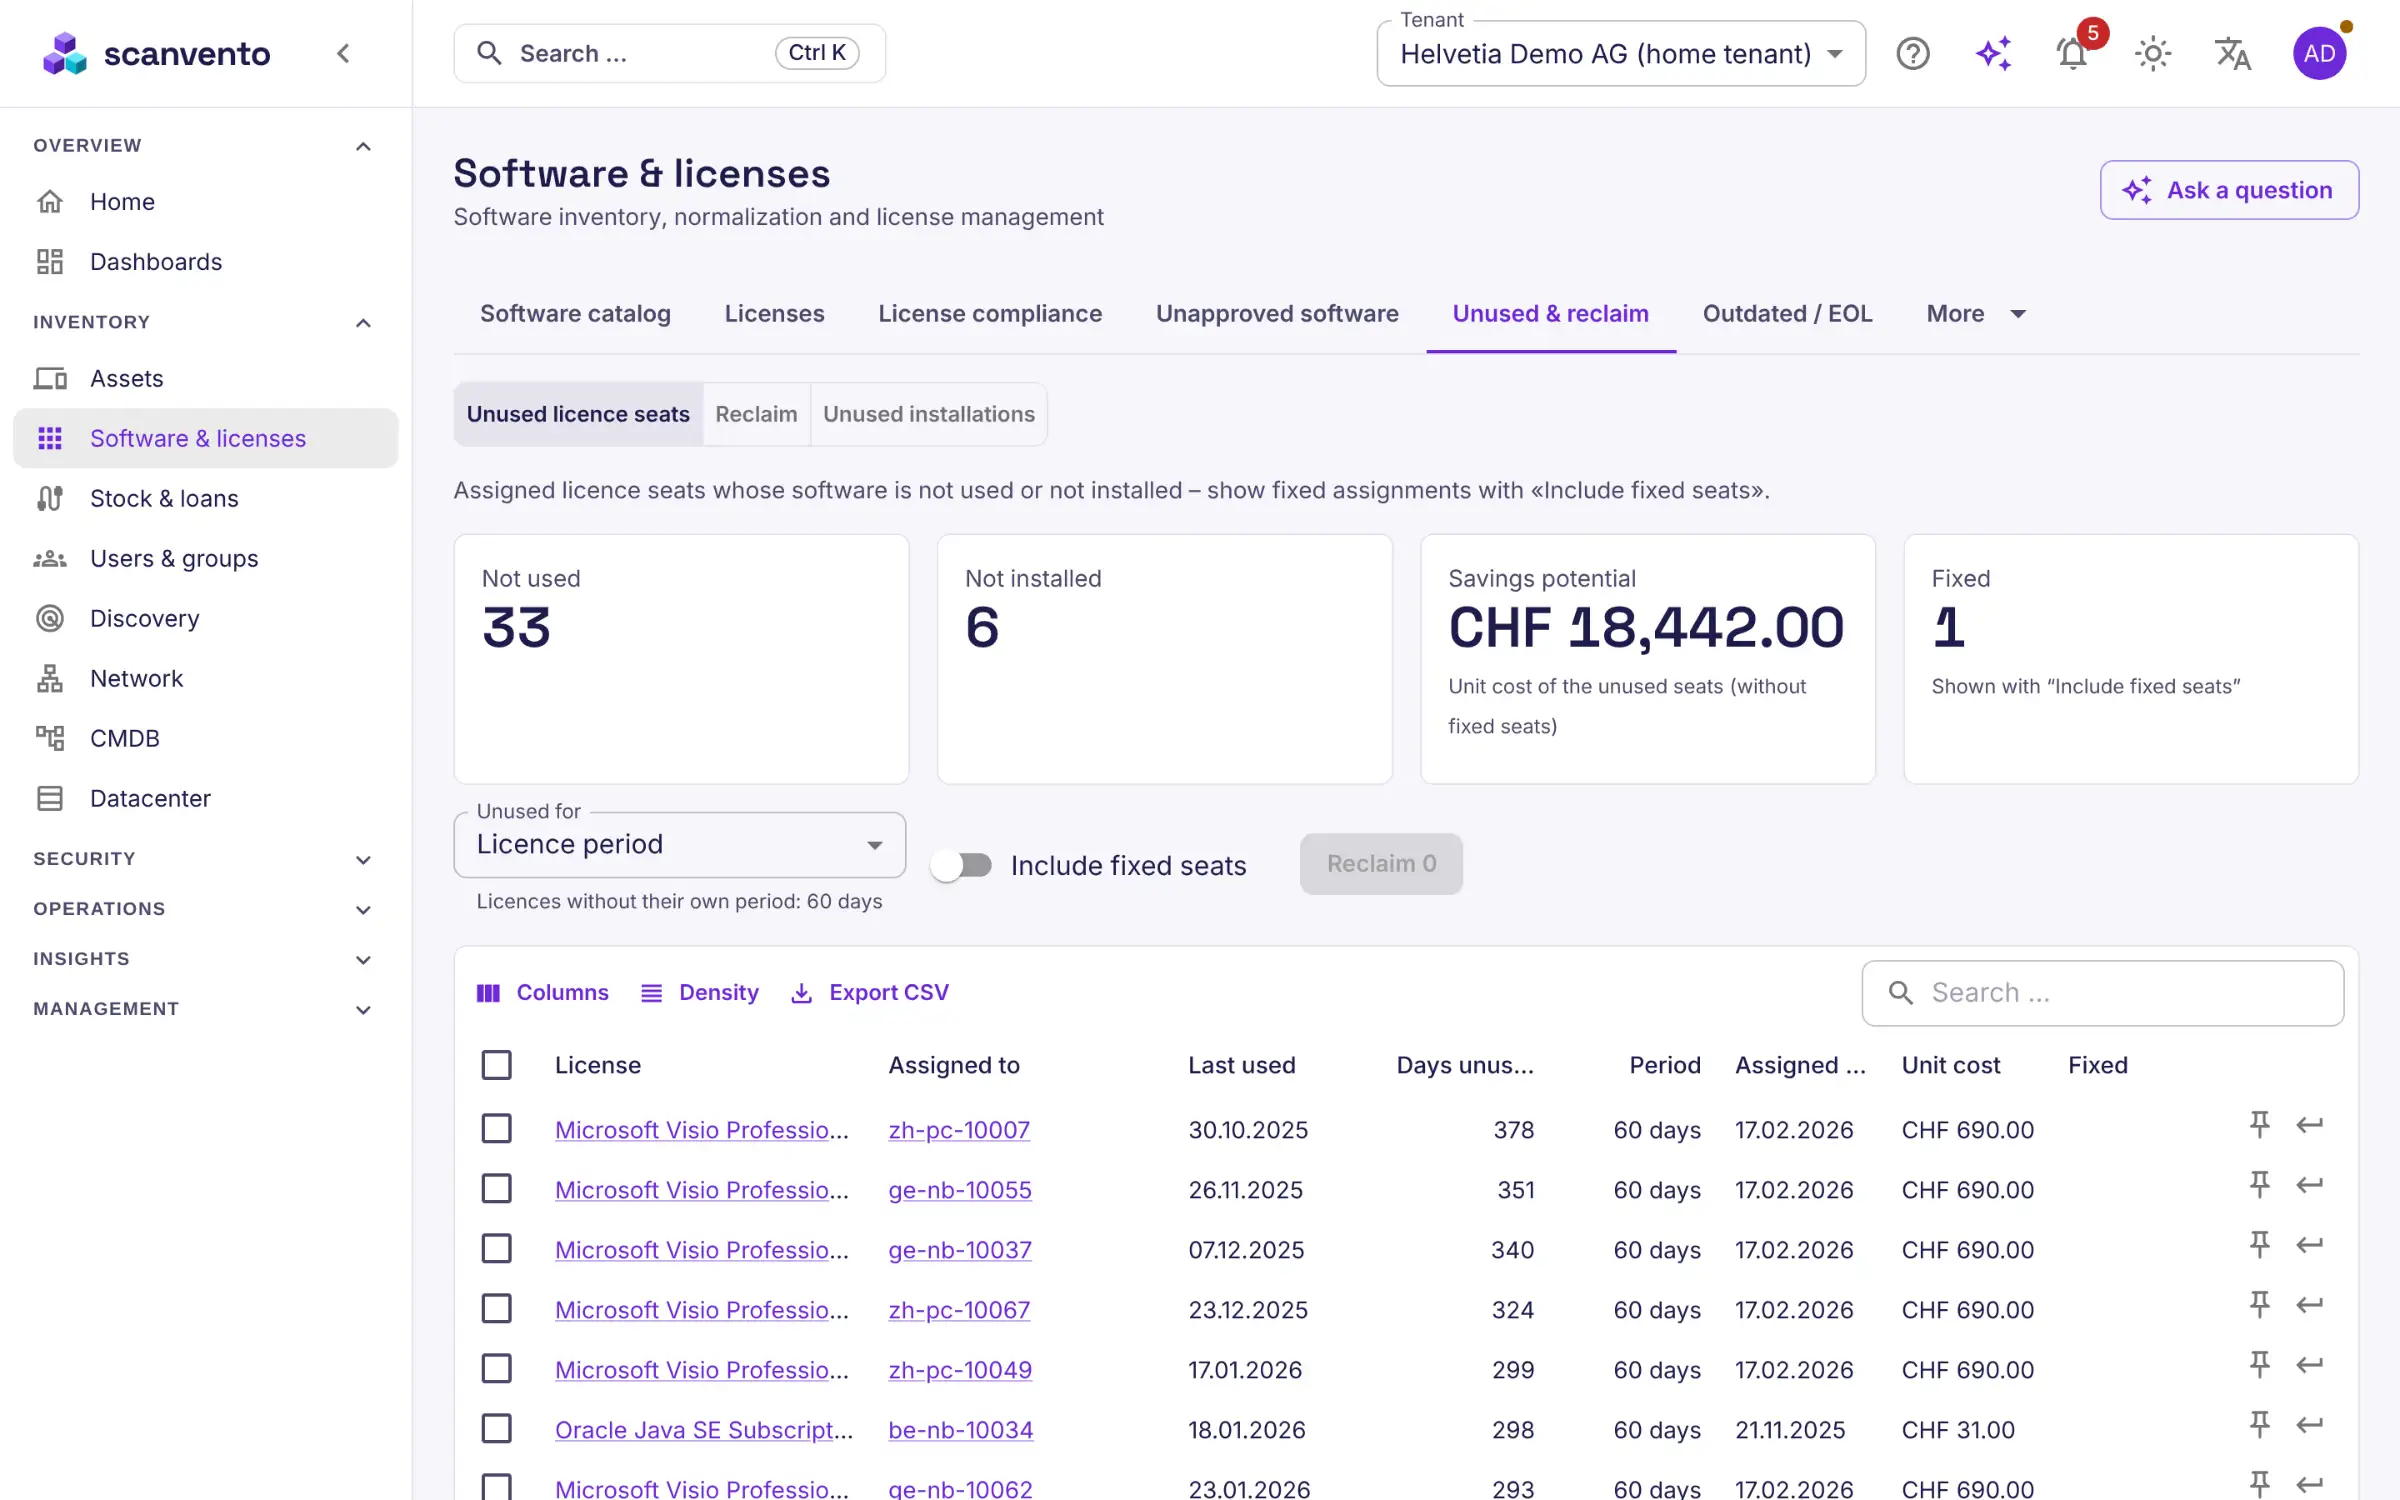
×
![Full Screenshot]()
App Metadata (Raw File)
{
"1.0.4": {
"healthy": true,
"supported": true,
"healthy_error": null,
"location": "/__w/apps/apps/trains/community/scanvento/1.0.4",
"last_update": "2026-11-13 18:53:10",
"required_features": [],
"human_version": "0.0.16_1.0.4",
"version": "1.0.4",
"app_metadata": {
"app_version": "0.0.16",
"capabilities": [],
"categories": [
"management"
],
"changelog_url": "https://scanvento.com/docs/en/changelog.html",
"date_added": "2026-11-13",
"description": "Scanvento is an IT asset management and discovery platform for hardware, software, licences, vulnerabilities and the asset lifecycle. Proprietary software, free edition up to 250 active assets without a licence file.",
"home": "https://scanvento.com",
"host_mounts": [],
"icon": "https://media.sys.truenas.net/apps/scanvento/icons/icon.svg",
"keywords": [
"asset",
"inventory",
"itam",
"cmdb",
"discovery",
"licence"
],
"lib_version": "2.3.19",
"lib_version_hash": "baa2e32ccdd8637a7604991b3f662e33c5ad10de47209b9fa8c6d2c2c916b5cf",
"maintainers": [
{
"email": "dev@truenas.com",
"name": "truenas",
"url": "https://www.truenas.com/"
}
],
"name": "scanvento",
"run_as_context": [
{
"description": "Container [postgres] runs as non-root user and group.",
"gid": 999,
"group_name": "Host group is [docker]",
"uid": 999,
"user_name": "Host user is [netdata]"
},
{
"description": "Container [redis] can run as any non-root user and group.",
"gid": 568,
"group_name": "Host group is [apps]",
"uid": 568,
"user_name": "Host user is [apps]"
},
{
"description": "Container [scanvento] can run as any non-root user and group.",
"gid": 568,
"group_name": "Host group is [apps]",
"uid": 568,
"user_name": "Host user is [apps]"
}
],
"screenshots": [
"https://media.sys.truenas.net/apps/scanvento/screenshots/screenshot1.webp",
"https://media.sys.truenas.net/apps/scanvento/screenshots/screenshot2.webp",
"https://media.sys.truenas.net/apps/scanvento/screenshots/screenshot3.webp",
"https://media.sys.truenas.net/apps/scanvento/screenshots/screenshot4.webp"
],
"sources": [
"https://apps.truenas.com/catalog/scanvento_community/",
"https://scanvento.com",
"https://scanvento.com/docs/en/"
],
"title": "Scanvento",
"train": "community",
"version": "1.0.4"
},
"schema": {
"groups": [
{
"name": "Scanvento Configuration",
"description": "Configure Scanvento"
},
{
"name": "User and Group Configuration",
"description": "Configure User and Group for Scanvento"
},
{
"name": "Network Configuration",
"description": "Configure Network for Scanvento"
},
{
"name": "Storage Configuration",
"description": "Configure Storage for Scanvento"
},
{
"name": "Labels Configuration",
"description": "Configure Labels for Scanvento"
},
{
"name": "Resources Configuration",
"description": "Configure Resources for Scanvento"
}
],
"questions": [
{
"variable": "TZ",
"group": "Scanvento Configuration",
"label": "Timezone",
"schema": {
"type": "string",
"default": "Etc/UTC",
"required": true,
"$ref": [
"definitions/timezone"
]
}
},
{
"variable": "scanvento",
"label": "",
"group": "Scanvento Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "postgres_image_selector",
"label": "Postgres Image (CAUTION)",
"description": "If you are changing this after the postgres directory has been initialized,</br>\nSTOP! and make sure you have a backup of your data.</br>\nChanging this will trigger an one way database upgrade.</br>\nYou can only select newer versions of postgres.</br>\nSelecting an older version will refuse to start.</br>\nIf something goes wrong, you will have to restore from backup.\n",
"schema": {
"type": "string",
"default": "postgres_18_image",
"required": true,
"enum": [
{
"value": "postgres_18_image",
"description": "Postgres 18"
}
]
}
},
{
"variable": "db_password",
"label": "Database Password",
"schema": {
"type": "string",
"default": "",
"required": true,
"private": true
}
},
{
"variable": "redis_password",
"label": "Redis Password",
"schema": {
"type": "string",
"default": "",
"required": true,
"private": true
}
},
{
"variable": "public_url",
"label": "Public URL",
"description": "The address users type in the browser, with scheme and port and without a path,</br>\ne.g. https://nas.example.lan:30584 (or http://\u2026 without a certificate).</br>\nUsed for links in e-mails, labels and alerts, and its host name as the passkey domain.\n",
"schema": {
"type": "uri",
"default": "",
"required": true
}
},
{
"variable": "admin_user",
"label": "Administrator User Name",
"description": "The first administrator, created on the first start.</br>\nIt is only used for the initial installation.\n",
"schema": {
"type": "string",
"default": "",
"required": true,
"immutable": true
}
},
{
"variable": "admin_email",
"label": "Administrator E-Mail",
"description": "E-mail address of the first administrator (optional).</br>\nIt is only used for the initial installation.\n",
"schema": {
"type": "string",
"default": ""
}
},
{
"variable": "admin_password",
"label": "Administrator Password",
"description": "Password of the first administrator, created on the first start.</br>\nAt least 12 characters, one of them neither a letter nor a digit.</br>\nChanging it later has no effect unless \"Reset Administrator Password\" is enabled.\n",
"schema": {
"type": "string",
"default": "",
"required": true,
"private": true,
"min_length": 12
}
},
{
"variable": "reset_admin_password",
"label": "Reset Administrator Password",
"description": "Emergency access: on every start, sets the administrator's password to the one above and lifts a lockout.</br>\nDisable it again once you have signed in.\n",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "encryption_master_key",
"label": "Encryption Master Key (back it up!)",
"description": "Base64 encoded 32 byte key that encrypts the stored credentials.</br>\nGenerate it once in the TrueNAS shell: openssl rand -base64 32</br>\nBACK IT UP outside the NAS. It can never be changed after the first start:\nthe credentials stored with it could no longer be decrypted.\n",
"schema": {
"type": "string",
"default": "",
"required": true,
"private": true,
"immutable": true,
"valid_chars": "^[A-Za-z0-9+/]{43}=$",
"valid_chars_error": "Must be 32 bytes in base64 (44 characters ending in \"=\")"
}
},
{
"variable": "jwt_signing_key",
"label": "JWT Signing Key",
"description": "Base64 encoded key (at least 32 bytes) that signs the sign-in tokens.</br>\nGenerate it once in the TrueNAS shell: openssl rand -base64 48</br>\nKeep it stable across updates; changing it signs everybody out.\n",
"schema": {
"type": "string",
"default": "",
"required": true,
"private": true,
"valid_chars": "^[A-Za-z0-9+/]{43,}={0,2}$",
"valid_chars_error": "Must be at least 32 bytes in base64"
}
},
{
"variable": "additional_envs",
"label": "Additional Environment Variables",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "env",
"label": "Environment Variable",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Name",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "value",
"label": "Value",
"schema": {
"type": "string"
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "run_as",
"label": "",
"group": "User and Group Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "user",
"label": "User ID",
"description": "The user id that Scanvento files will be owned by.",
"schema": {
"type": "int",
"min": 568,
"default": 568,
"required": true
}
},
{
"variable": "group",
"label": "Group ID",
"description": "The group id that Scanvento files will be owned by.",
"schema": {
"type": "int",
"min": 568,
"default": 568,
"required": true
}
}
]
}
},
{
"variable": "network",
"label": "",
"group": "Network Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "web_port",
"label": "WebUI Port",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "bind_mode",
"label": "Port Bind Mode",
"description": "The port bind mode.</br>\n- Publish: The port will be published on the host for external access.</br>\n- Expose: The port will be exposed for inter-container communication.</br>\n- None: The port will not be exposed or published.</br>\nNote: If the Dockerfile defines an EXPOSE directive,\nthe port will still be exposed for inter-container communication regardless of this setting.\n",
"schema": {
"type": "string",
"default": "published",
"enum": [
{
"value": "published",
"description": "Publish port on the host for external access"
},
{
"value": "exposed",
"description": "Expose port for inter-container communication"
},
{
"value": "",
"description": "None"
}
]
}
},
{
"variable": "port_number",
"label": "Port Number",
"schema": {
"type": "int",
"default": 30584,
"min": 1,
"max": 65535,
"required": true
}
},
{
"variable": "host_ips",
"label": "Host IPs",
"description": "IPs on the host to bind this port",
"schema": {
"type": "list",
"show_if": [
[
"bind_mode",
"=",
"published"
]
],
"default": [],
"items": [
{
"variable": "host_ip",
"label": "Host IP",
"schema": {
"type": "string",
"required": true,
"$ref": [
"definitions/node_bind_ip"
]
}
}
]
}
}
]
}
},
{
"variable": "certificate_id",
"label": "Certificate ID",
"description": "The certificate for HTTPS on the WebUI port.</br>\nWithout one, the WebUI port uses plain HTTP.\n",
"schema": {
"type": "int",
"null": true,
"$ref": [
"definitions/certificate"
]
}
},
{
"variable": "networks",
"label": "Networks",
"description": "The docker networks to join",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "network",
"label": "Network",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Name",
"description": "The name of the network to join.</br>\nThe network must already exist.\n",
"schema": {
"type": "string",
"default": "",
"required": true
}
},
{
"variable": "containers",
"label": "Containers",
"description": "The containers to add to this network.",
"schema": {
"type": "list",
"items": [
{
"variable": "container",
"label": "Container",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "name",
"label": "Container Name",
"schema": {
"type": "string",
"required": true,
"enum": [
{
"value": "scanvento",
"description": "scanvento"
},
{
"value": "postgres",
"description": "postgres"
},
{
"value": "redis",
"description": "redis"
}
]
}
},
{
"variable": "config",
"label": "Container Network Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "aliases",
"label": "Aliases (Optional)",
"description": "The network aliases to use for this container on this network.",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "alias",
"label": "Alias",
"schema": {
"type": "string"
}
}
]
}
},
{
"variable": "interface_name",
"label": "Interface Name (Optional)",
"description": "The network interface name to use for this network",
"schema": {
"type": "string"
}
},
{
"variable": "mac_address",
"label": "MAC Address (Optional)",
"description": "The MAC address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "ipv4_address",
"label": "IPv4 Address (Optional)",
"description": "The IPv4 address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "ipv6_address",
"label": "IPv6 Address (Optional)",
"description": "The IPv6 address to use for this network interface.",
"schema": {
"type": "string"
}
},
{
"variable": "gw_priority",
"label": "Gateway Priority (Optional)",
"description": "Indicates the priority of the gateway for this network interface.",
"schema": {
"type": "int",
"null": true
}
},
{
"variable": "priority",
"label": "Priority (Optional)",
"description": "Indicates in which order Compose connects the service\u2019s containers to its networks.",
"schema": {
"type": "int",
"null": true
}
}
]
}
}
]
}
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "storage",
"label": "",
"group": "Storage Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "postgres_data",
"label": "Scanvento Postgres Data Storage",
"description": "The path to store Scanvento Postgres Data.",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "type",
"label": "Type",
"description": "ixVolume: Is dataset created automatically by the system.</br>\nHost Path: Is a path that already exists on the system.\n",
"schema": {
"type": "string",
"required": true,
"default": "ix_volume",
"enum": [
{
"value": "host_path",
"description": "Host Path (Path that already exists on the system)"
},
{
"value": "ix_volume",
"description": "ixVolume (Dataset created automatically by the system)"
}
]
}
},
{
"variable": "ix_volume_config",
"label": "ixVolume Configuration",
"description": "The configuration for the ixVolume dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"ix_volume"
]
],
"$ref": [
"normalize/ix_volume"
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "dataset_name",
"label": "Dataset Name",
"description": "The name of the dataset to use for storage.",
"schema": {
"type": "string",
"required": true,
"hidden": true,
"default": "postgres_data"
}
},
{
"variable": "acl_entries",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": []
}
}
]
}
},
{
"variable": "host_path_config",
"label": "Host Path Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"host_path"
]
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "acl",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
},
{
"variable": "path",
"label": "Host Path",
"description": "The host path to use for storage.",
"schema": {
"type": "hostpath",
"show_if": [
[
"acl_enable",
"=",
false
]
],
"required": true
}
},
{
"variable": "auto_permissions",
"label": "Automatic Permissions",
"description": "Automatically set permissions for the host path.\nEnabling this, will check the top level directory,</br>\nIf it finds incorrect permissions, it will `chown` the\nhost path to the user and group required for the\npostgres container.\n",
"schema": {
"type": "boolean",
"default": false,
"show_if": [
[
"acl_enable",
"=",
false
]
]
}
}
]
}
}
]
}
},
{
"variable": "additional_storage",
"label": "Additional Storage",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "storage_entry",
"label": "Storage Entry",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "type",
"label": "Type",
"description": "ixVolume: Is dataset created automatically by the system.</br>\nHost Path: Is a path that already exists on the system.</br>\nSMB Share: Is a SMB share that is mounted to as a volume.</br>\nNFS Share: Is a NFS share that is mounted to as a volume.\n",
"schema": {
"type": "string",
"required": true,
"default": "ix_volume",
"enum": [
{
"value": "host_path",
"description": "Host Path (Path that already exists on the system)"
},
{
"value": "ix_volume",
"description": "ixVolume (Dataset created automatically by the system)"
},
{
"value": "cifs",
"description": "SMB/CIFS Share (Mounts a volume to a SMB share)"
},
{
"value": "nfs",
"description": "NFS Share (Mounts a volume to a NFS share)"
}
]
}
},
{
"variable": "read_only",
"label": "Read Only",
"description": "Mount the volume as read only.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "mount_path",
"label": "Mount Path",
"description": "The path inside the container to mount the storage.",
"schema": {
"type": "path",
"required": true
}
},
{
"variable": "host_path_config",
"label": "Host Path Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"host_path"
]
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "acl",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
},
{
"variable": "path",
"label": "Host Path",
"description": "The host path to use for storage.",
"schema": {
"type": "hostpath",
"show_if": [
[
"acl_enable",
"=",
false
]
],
"required": true
}
}
]
}
},
{
"variable": "ix_volume_config",
"label": "ixVolume Configuration",
"description": "The configuration for the ixVolume dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"ix_volume"
]
],
"$ref": [
"normalize/ix_volume"
],
"attrs": [
{
"variable": "acl_enable",
"label": "Enable ACL",
"description": "Enable ACL for the storage.",
"schema": {
"type": "boolean",
"default": false
}
},
{
"variable": "dataset_name",
"label": "Dataset Name",
"description": "The name of the dataset to use for storage.",
"schema": {
"type": "string",
"required": true,
"default": "storage_entry"
}
},
{
"variable": "acl_entries",
"label": "ACL Configuration",
"schema": {
"type": "dict",
"show_if": [
[
"acl_enable",
"=",
true
]
],
"attrs": [],
"$ref": [
"normalize/acl"
]
}
}
]
}
},
{
"variable": "cifs_config",
"label": "SMB Configuration",
"description": "The configuration for the SMB dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"cifs"
]
],
"attrs": [
{
"variable": "server",
"label": "Server",
"description": "The server to mount the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "path",
"label": "Path",
"description": "The path to mount the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "username",
"label": "Username",
"description": "The username to use for the SMB share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "password",
"label": "Password",
"description": "The password to use for the SMB share.",
"schema": {
"type": "string",
"required": true,
"private": true
}
},
{
"variable": "domain",
"label": "Domain",
"description": "The domain to use for the SMB share.",
"schema": {
"type": "string"
}
}
]
}
},
{
"variable": "nfs_config",
"label": "NFS Configuration",
"description": "The configuration for the NFS dataset.",
"schema": {
"type": "dict",
"show_if": [
[
"type",
"=",
"nfs"
]
],
"attrs": [
{
"variable": "server",
"label": "Server",
"description": "The server to mount the NFS share.",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "path",
"label": "Path",
"description": "The path to mount the NFS share.",
"schema": {
"type": "string",
"required": true
}
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "labels",
"label": "",
"group": "Labels Configuration",
"schema": {
"type": "list",
"default": [],
"items": [
{
"variable": "label",
"label": "Label",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "key",
"label": "Key",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "value",
"label": "Value",
"schema": {
"type": "string",
"required": true
}
},
{
"variable": "containers",
"label": "Containers",
"description": "Containers where the label should be applied",
"schema": {
"type": "list",
"items": [
{
"variable": "container",
"label": "Container",
"schema": {
"type": "string",
"required": true,
"enum": [
{
"value": "scanvento",
"description": "scanvento"
},
{
"value": "postgres",
"description": "postgres"
},
{
"value": "redis",
"description": "redis"
}
]
}
}
]
}
}
]
}
}
]
}
},
{
"variable": "resources",
"label": "",
"group": "Resources Configuration",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "limits",
"label": "Limits",
"schema": {
"type": "dict",
"attrs": [
{
"variable": "cpus",
"label": "CPUs",
"description": "CPUs limit for Scanvento.",
"schema": {
"type": "int",
"default": 2,
"required": true
}
},
{
"variable": "memory",
"label": "Memory (in MB)",
"description": "Memory limit for Scanvento.",
"schema": {
"type": "int",
"default": 4096,
"required": true
}
}
]
}
}
]
}
}
]
},
"readme": "<h1>Scanvento</h1> <p><a href=\"https://scanvento.com\">Scanvento</a> is an IT asset management and discovery platform: network discovery and agents, hardware and software inventory, licences, contracts, vulnerabilities and the asset lifecycle in one web application.</p> <p>Scanvento is proprietary software, not open source. Without a licence file it runs as the free edition (every module except MSP, one tenant, up to 250 active assets, no expiry); larger installations need a licence.</p>",
"changelog": null,
"chart_metadata": {
"app_version": "0.0.16",
"capabilities": [],
"categories": [
"management"
],
"changelog_url": "https://scanvento.com/docs/en/changelog.html",
"date_added": "2026-11-13",
"description": "Scanvento is an IT asset management and discovery platform for hardware, software, licences, vulnerabilities and the asset lifecycle. Proprietary software, free edition up to 250 active assets without a licence file.",
"home": "https://scanvento.com",
"host_mounts": [],
"icon": "https://media.sys.truenas.net/apps/scanvento/icons/icon.svg",
"keywords": [
"asset",
"inventory",
"itam",
"cmdb",
"discovery",
"licence"
],
"lib_version": "2.3.19",
"lib_version_hash": "baa2e32ccdd8637a7604991b3f662e33c5ad10de47209b9fa8c6d2c2c916b5cf",
"maintainers": [
{
"email": "dev@truenas.com",
"name": "truenas",
"url": "https://www.truenas.com/"
}
],
"name": "scanvento",
"run_as_context": [
{
"description": "Container [postgres] runs as non-root user and group.",
"gid": 999,
"group_name": "Host group is [docker]",
"uid": 999,
"user_name": "Host user is [netdata]"
},
{
"description": "Container [redis] can run as any non-root user and group.",
"gid": 568,
"group_name": "Host group is [apps]",
"uid": 568,
"user_name": "Host user is [apps]"
},
{
"description": "Container [scanvento] can run as any non-root user and group.",
"gid": 568,
"group_name": "Host group is [apps]",
"uid": 568,
"user_name": "Host user is [apps]"
}
],
"screenshots": [
"https://media.sys.truenas.net/apps/scanvento/screenshots/screenshot1.webp",
"https://media.sys.truenas.net/apps/scanvento/screenshots/screenshot2.webp",
"https://media.sys.truenas.net/apps/scanvento/screenshots/screenshot3.webp",
"https://media.sys.truenas.net/apps/scanvento/screenshots/screenshot4.webp"
],
"sources": [
"https://apps.truenas.com/catalog/scanvento_community/",
"https://scanvento.com",
"https://scanvento.com/docs/en/"
],
"title": "Scanvento",
"train": "community",
"version": "1.0.4"
}
}
}Support, maintenance, and documentation for applications within the Community catalog is handled by the TrueNAS community. The TrueNAS Applications Market hosts but does not validate or maintain any linked resources associated with this app.
There currently aren’t any resources available for this application!
Please help the TrueNAS community add resources here or discuss this application in the TrueNAS Community forum.